Third-Party Risk Management

Your vendor's breach
is your headline

Every vendor with access to your systems is part of your attack surface. Most teams manage that exposure with spreadsheets and annual questionnaires. Alvor gives every vendor relationship a tier, a scored assessment, a reassessment date set by that tier and a complete audit trail.

LOWMEDHIGHCRITCRITHIGHMEDLOW121133362541

Procurement onboarded them. Security found out later.

The security analyst

One structured assessment, not a questionnaire you rebuild each time.

  • One structured assessment, weighted across the domains that matter
  • A tier derived from the intake, which sets how often they are reassessed
  • Findings with severity deadlines and a nightly breach sweep

The business requester

File the vendor before it exists, in a form built for you.

  • Justification, services and contract details captured at intake
  • Triaged and approved by someone else: the requester never approves
  • No security vocabulary required to complete it

The vendor

Answer in a portal, not a spreadsheet attached to an email.

  • A hardened external portal with a rotating link and an emailed code
  • Autosave and evidence upload while they work
  • Every submission writes an entry to the hash-chained audit log

Every vendor moves through the same six stages.

Every vendor relationship follows the same structured path from onboarding request through to a formal, documented decision. No informal approvals. No gaps in the record.

01

Vendor onboarding triggered

A new vendor request or renewal is submitted with business context, data access scope, and the estimated go-live date. Alvor creates the vendor record and starts the SLA clock immediately - no vendor sits in a queue without an owner.

Vendor recordBusiness contextAccess scope

What that looks like on screen.

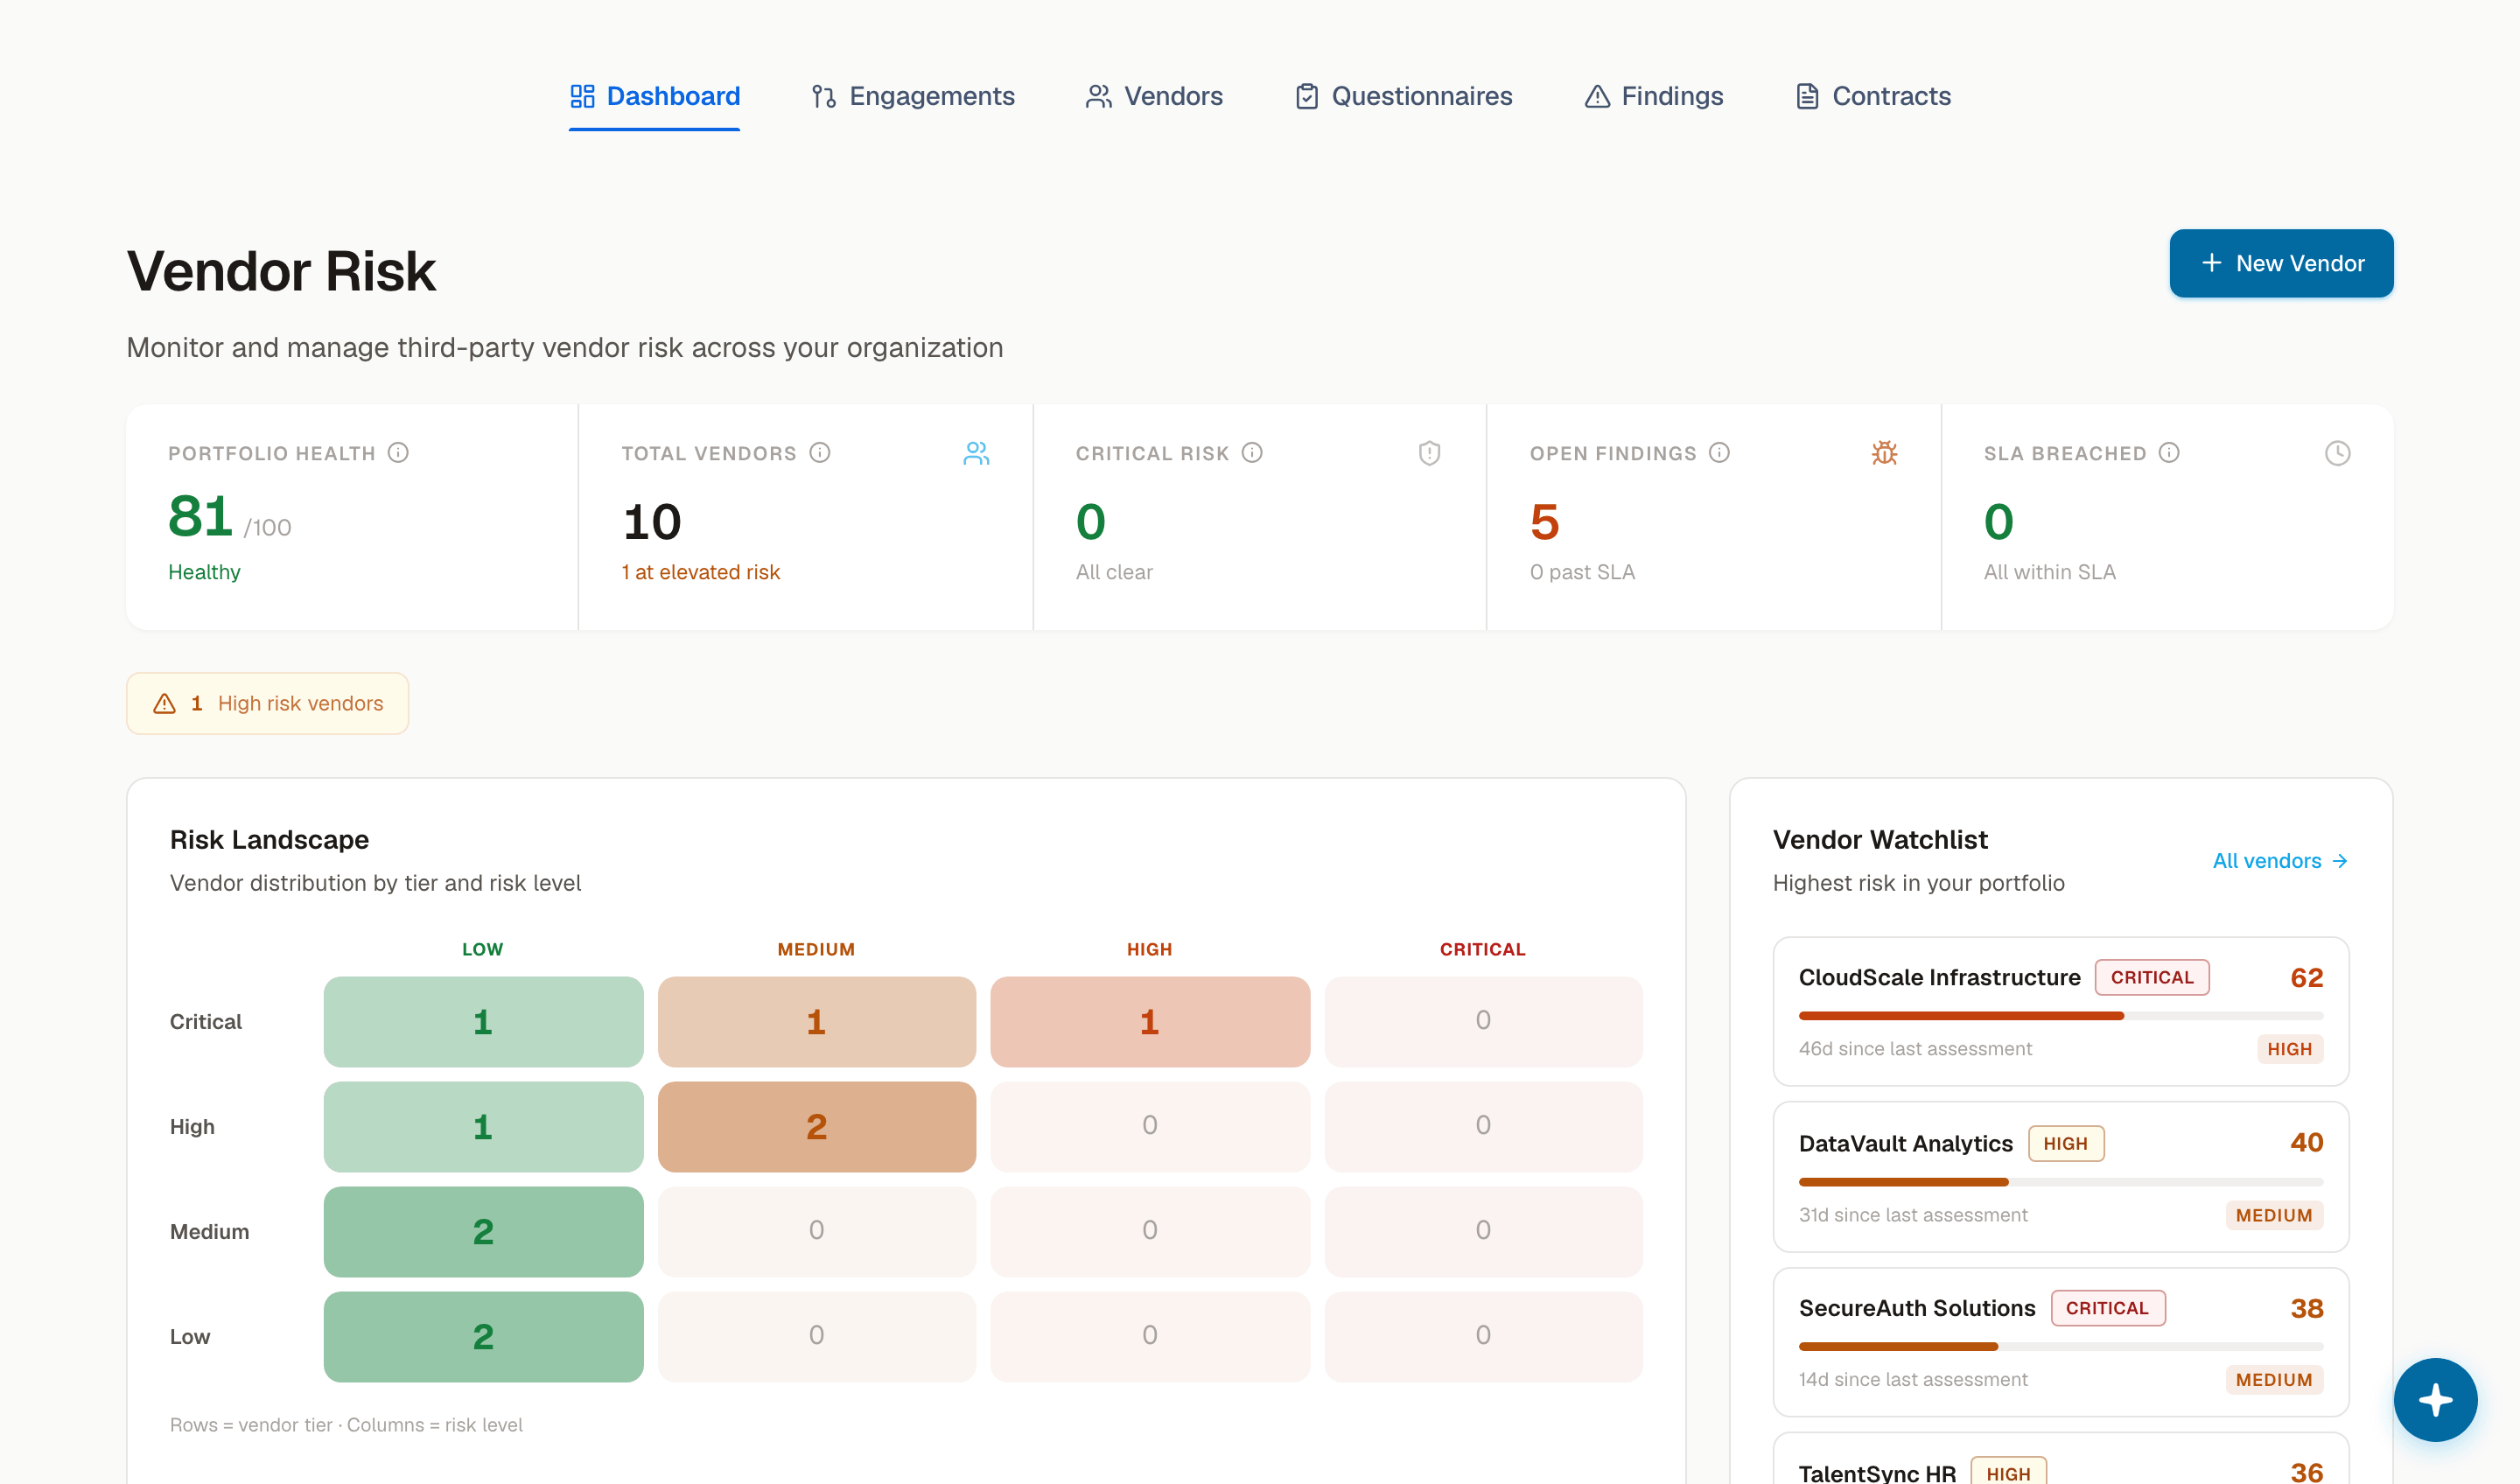
01 · The portfolio

Every supplier, with the state of its assessment

Who has been assessed, who is overdue, and where the residual risk sits across the portfolio. The reassessment cadence comes from the tier the intake produced, so nothing quietly ages out of review. Sub-processors are grouped across vendors, so one provider behind several Critical or High vendors shows up as a concentration.

app.alvor.io/vendors
Every supplier, with the state of its assessment

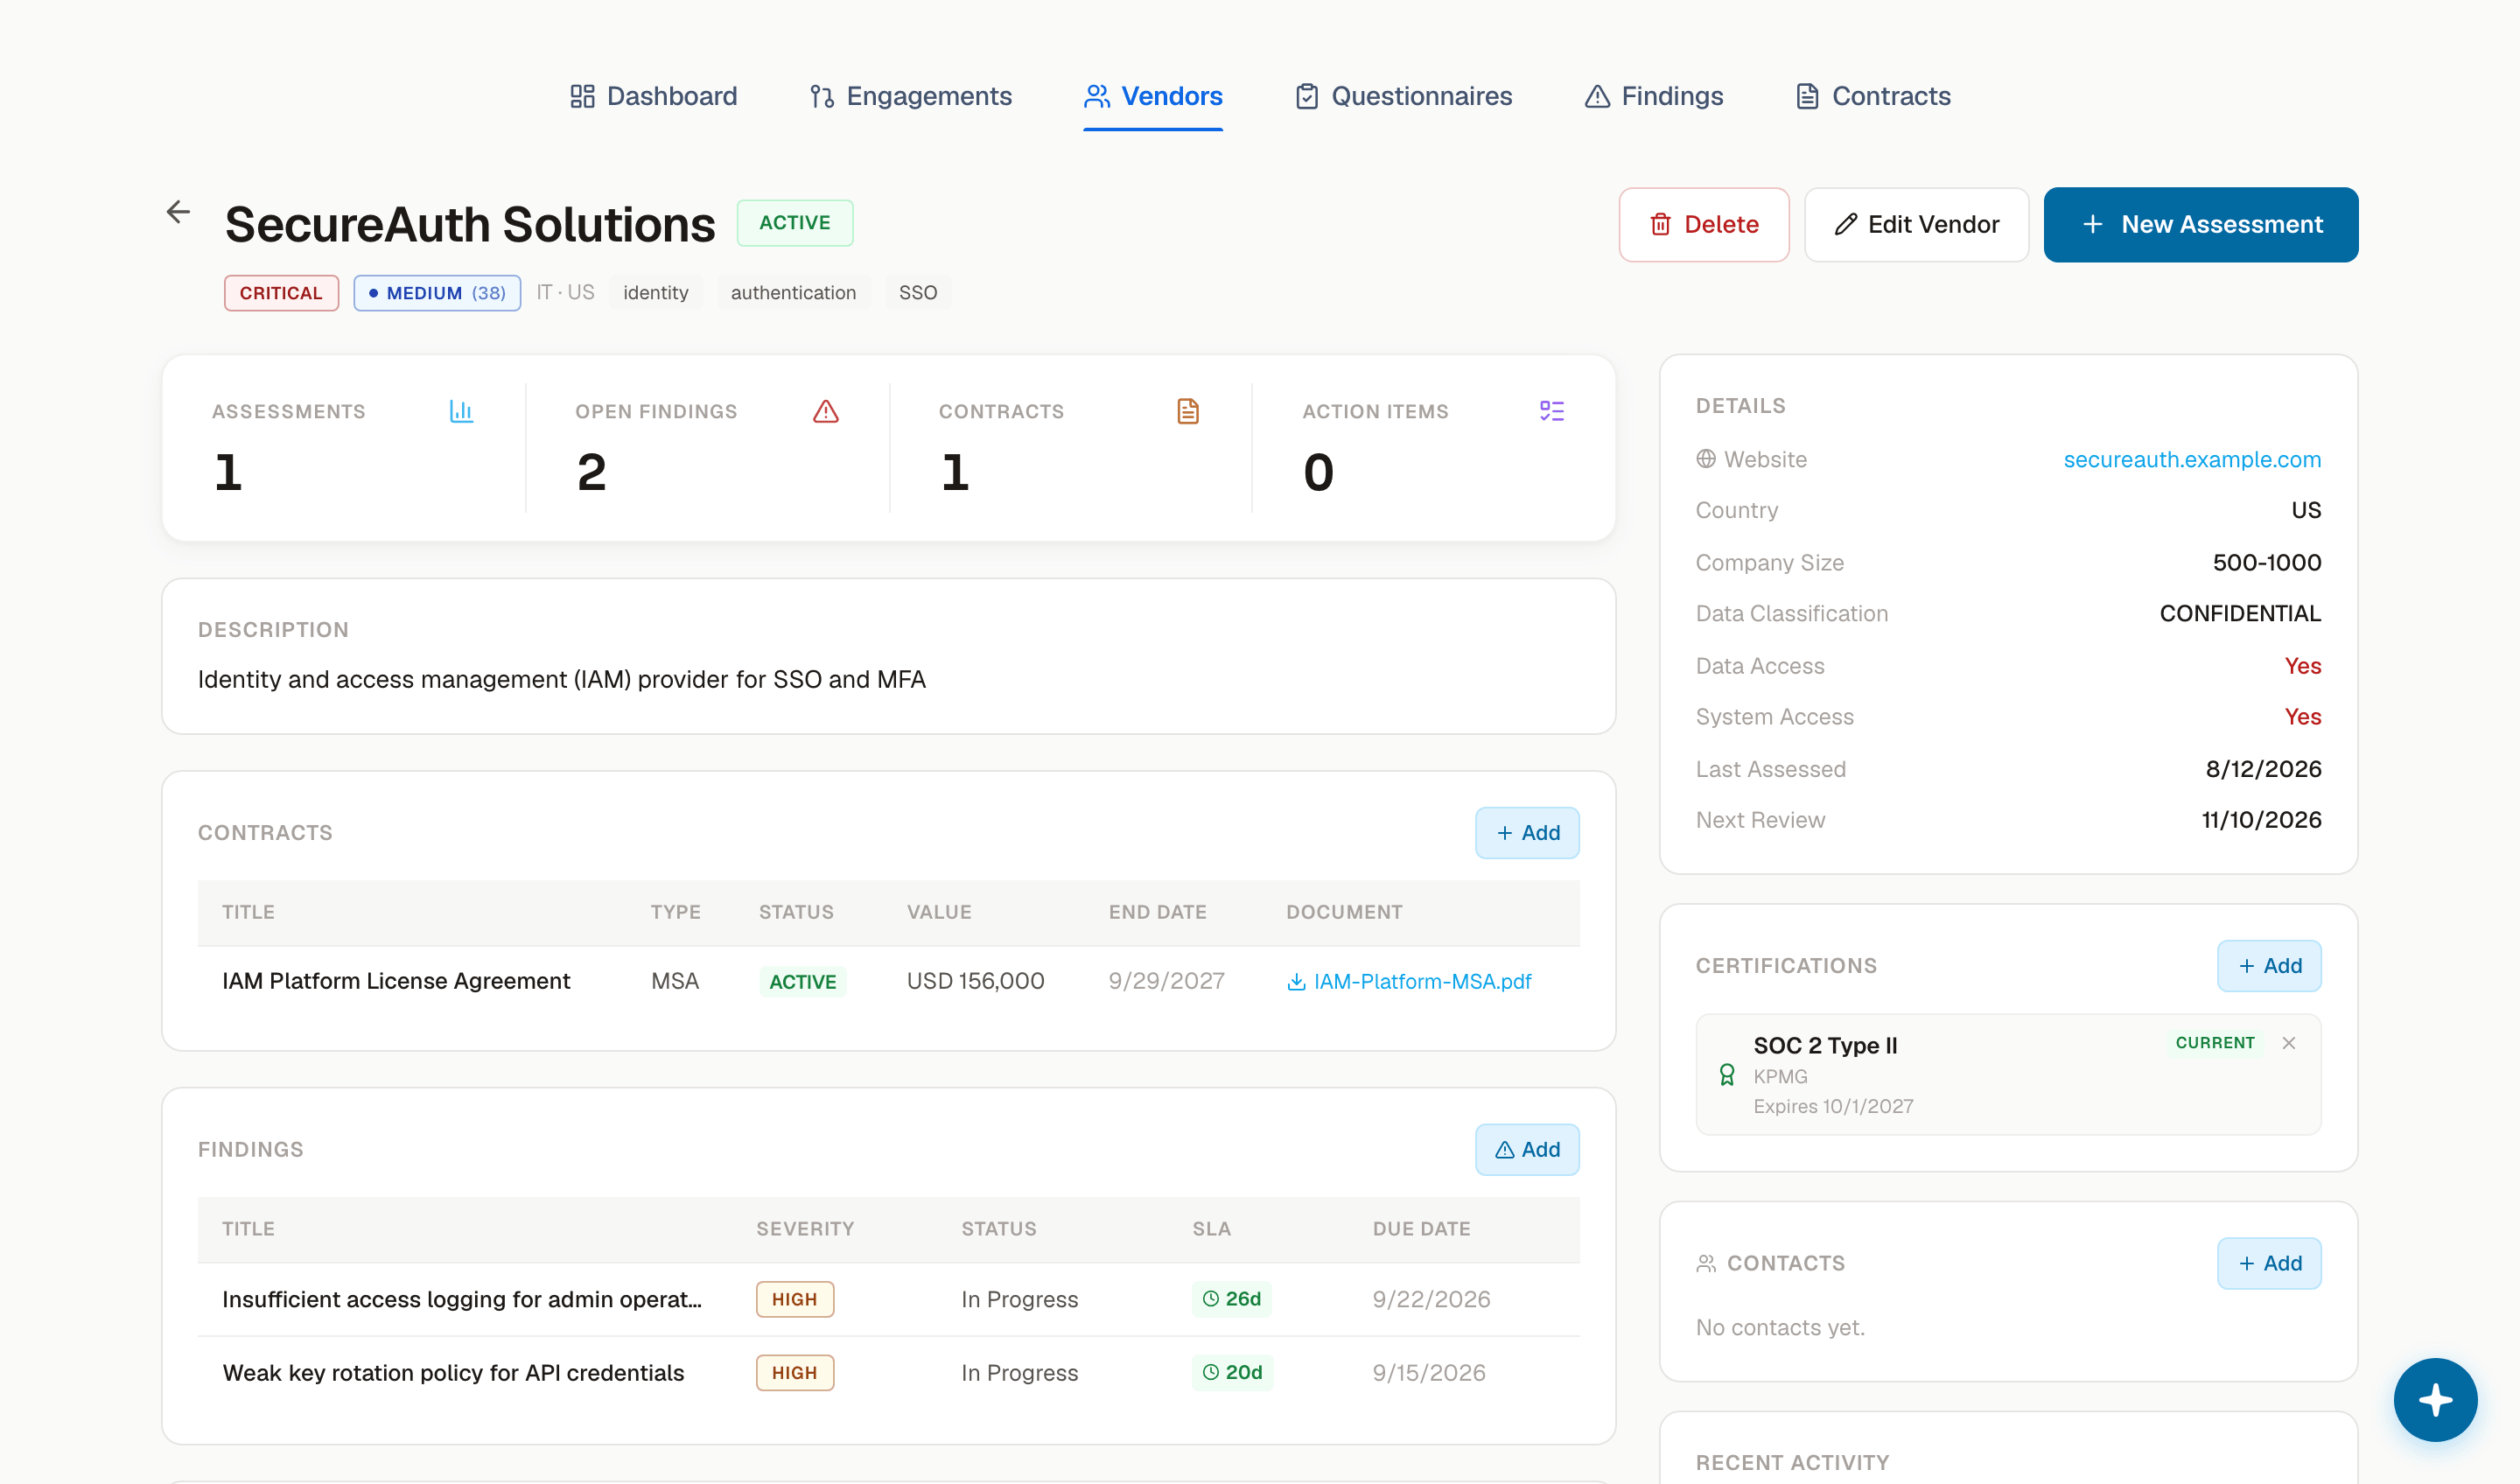
02 · A single vendor

The whole engagement on one record

Contacts, contracts, certifications, the scored assessment and its findings. Each contract records its incident-notification window in hours and which protective clauses are present. Residual risk is accepted only by the person named to accept it, with conditions and an expiry. When the relationship ends, an offboarding checklist covers access, data return, the destruction certificate and the contract.

app.alvor.io/vendors/detail
The whole engagement on one record

All vendors and risk levels in one view.

A live portfolio dashboard that tells you exactly where your vendor risk is concentrated - without asking you to build it yourself in a pivot table.

  • Risk matrix across all vendor tiers and risk levels
  • SLA tracking with breach alerts before deadlines pass
  • Portfolio health score updated after every assessment
  • Findings dashboard linked to vendor and remediation owner

Total Vendors

84

Critical Tier

6

Open Findings

23

SLA Breached

3

Low

Med

High

Crit

CRIT

1
2
1

HIGH

1
3
3

MED

3
6
2

LOW

5
4
1

Approval status

Approved (61)
Conditional (15)
Under Review (8)

Eight risk domains roll up into one score.

Every assessment scores the vendor across eight security domains, weighted by their access type. The aggregate score drives the decision - with full transparency into which domain pulled it down.

  • Domains weighted by data access and system privileges
  • Score history shows improvement or regression over time
  • Findings linked directly to the domain that triggered them
  • Certification evidence stored and tracked for expiry
SA

Security Architecture

Network segmentation, encryption standards, and infrastructure hardening practices

AC

Access Control

Identity management, MFA enforcement, and privileged access governance policies

DP

Data Protection

Classification policies, at-rest and in-transit encryption, and retention controls

IR

Incident Response

Detection capabilities, response playbooks, and breach notification timelines

BC

Business Continuity

Recovery time objectives, tested disaster recovery plans, and geographic redundancy

SP

Sub-Processor Risk

Visibility into subcontractors, nested vendor policies, and supply chain controls

CM

Compliance

Active certifications (SOC 2, ISO 27001, PCI), audit histories, and regulatory standing

PS

Physical Security

Facility access controls, data centre certifications, and physical access logging

Vendor review that finishes, and comes back around.

The hard part of third-party risk is not the questionnaire. It is that the process stalls the moment it leaves your organisation.

Instead of

A questionnaire in a spreadsheet over email

Version confusion, no audit trail, and evidence attached to a thread.

In Alvor

A hardened external portal with a one-time code, autosave and evidence upload, writing every submission to the audit log.

Instead of

Onboarding with no security step

The vendor is live because the procurement form never asked the question.

In Alvor

Intake filed before the vendor exists, triaged and approved by someone other than the requester.

Instead of

A review that happens once

Assessed at signing, then never looked at again until something goes wrong.

In Alvor

A tier derived from the intake that sets the reassessment cadence, with findings carrying severity deadlines and a nightly breach sweep.

These are the exact links in the data model.

Named precisely, because “everything connects to everything” is not a claim anyone can check. Select any module to see its links.

01Set the program
02Design new systems
03Prove controls work
04Manage risk, vendors and continuity
RegisterThe register the rest stands on
Runs onYour own instance
Dedicated cloudOne instance for your company, in your region
On-premiseThe same platform, on your own servers
Air-gappedFully disconnected, with a self-hosted model

Links the product makes today

Third-Party Risk Management links to

Business ContinuityA business process can declare a vendor as a typed dependency with its own criticality. This is the only cross-module link from a vendor record.
AI AssistantThe assistant reads vendors, findings, assessments and requests. Creating a finding or changing its status is proposed as an approval card a person accepts.

Further reading

Thinking on vendor and third-party risk.

Third-Party Risk Management

Stop trusting vendors on faith. Start assessing them on evidence.

Alvor brings structure, consistency, and a complete audit trail to every third-party relationship - from the first request to the annual renewal. Your vendors, your risk, your record.