Data centre physical security audit checklist, mapped to the PSPF, ISM, ISO 27001 and SOC 2
A data centre physical security audit checklist, each item mapped to the PSPF, ISM controls, CIRMP s 11, ISO 27001 A.7 and SOC 2 CC6.4, from site to rack.
Compliance
You answer to more than one framework at once. Alvor maps a control once and reuses its evidence across every framework that asks: 36 packs in the library, 7 with verbatim control text, and 18 automated checks across five providers.
Who it is for
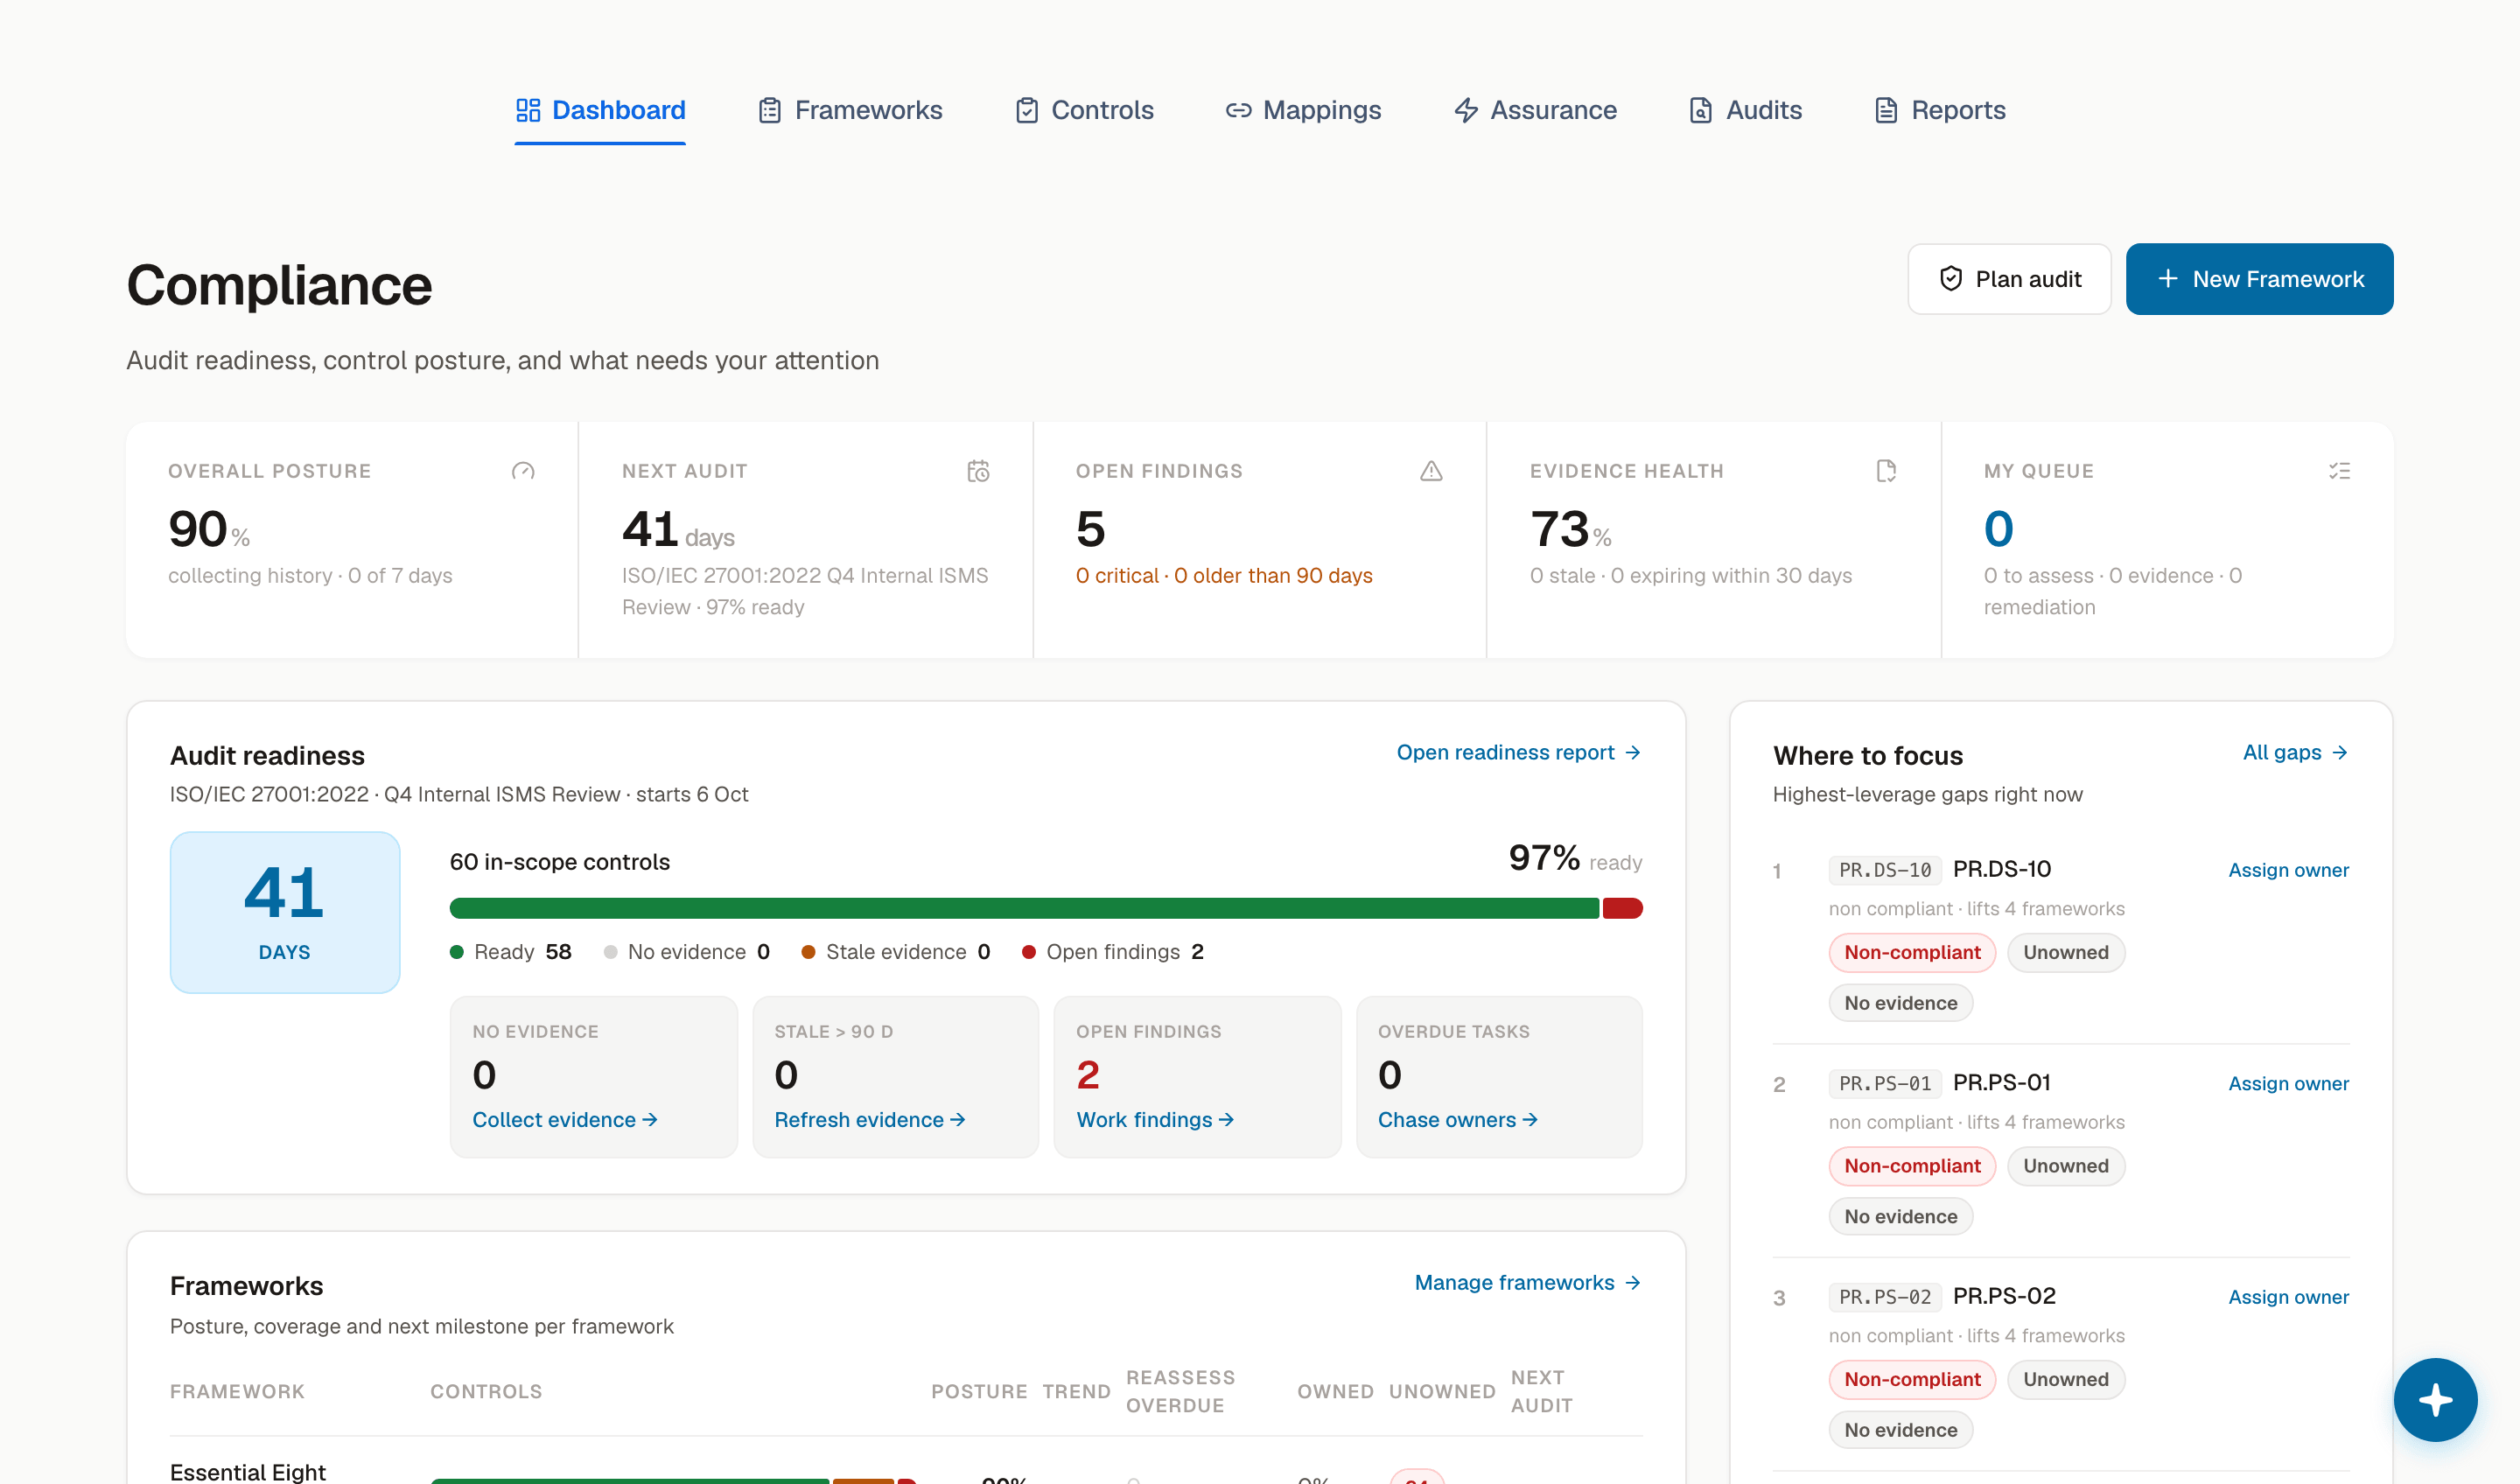
Five tiles that each deep-link to the records behind the number.
Install the framework, and the control text is already there.
Scope, assess, and turn findings into work that has an owner.
Cross-framework mapping
One control implementation satisfies requirements across every framework. See exactly which standards are covered - and which gaps remain.
| Control | SOC 2 | ISO 27001 | NIST CSF | PCI DSS | HIPAA | GDPR |
|---|---|---|---|---|---|---|
| Access Control | ||||||
| Encryption at Rest | ||||||
| Incident Response | ||||||
| Change Management | ||||||
| Logging & Monitoring | ||||||
| Vendor Management |
The product
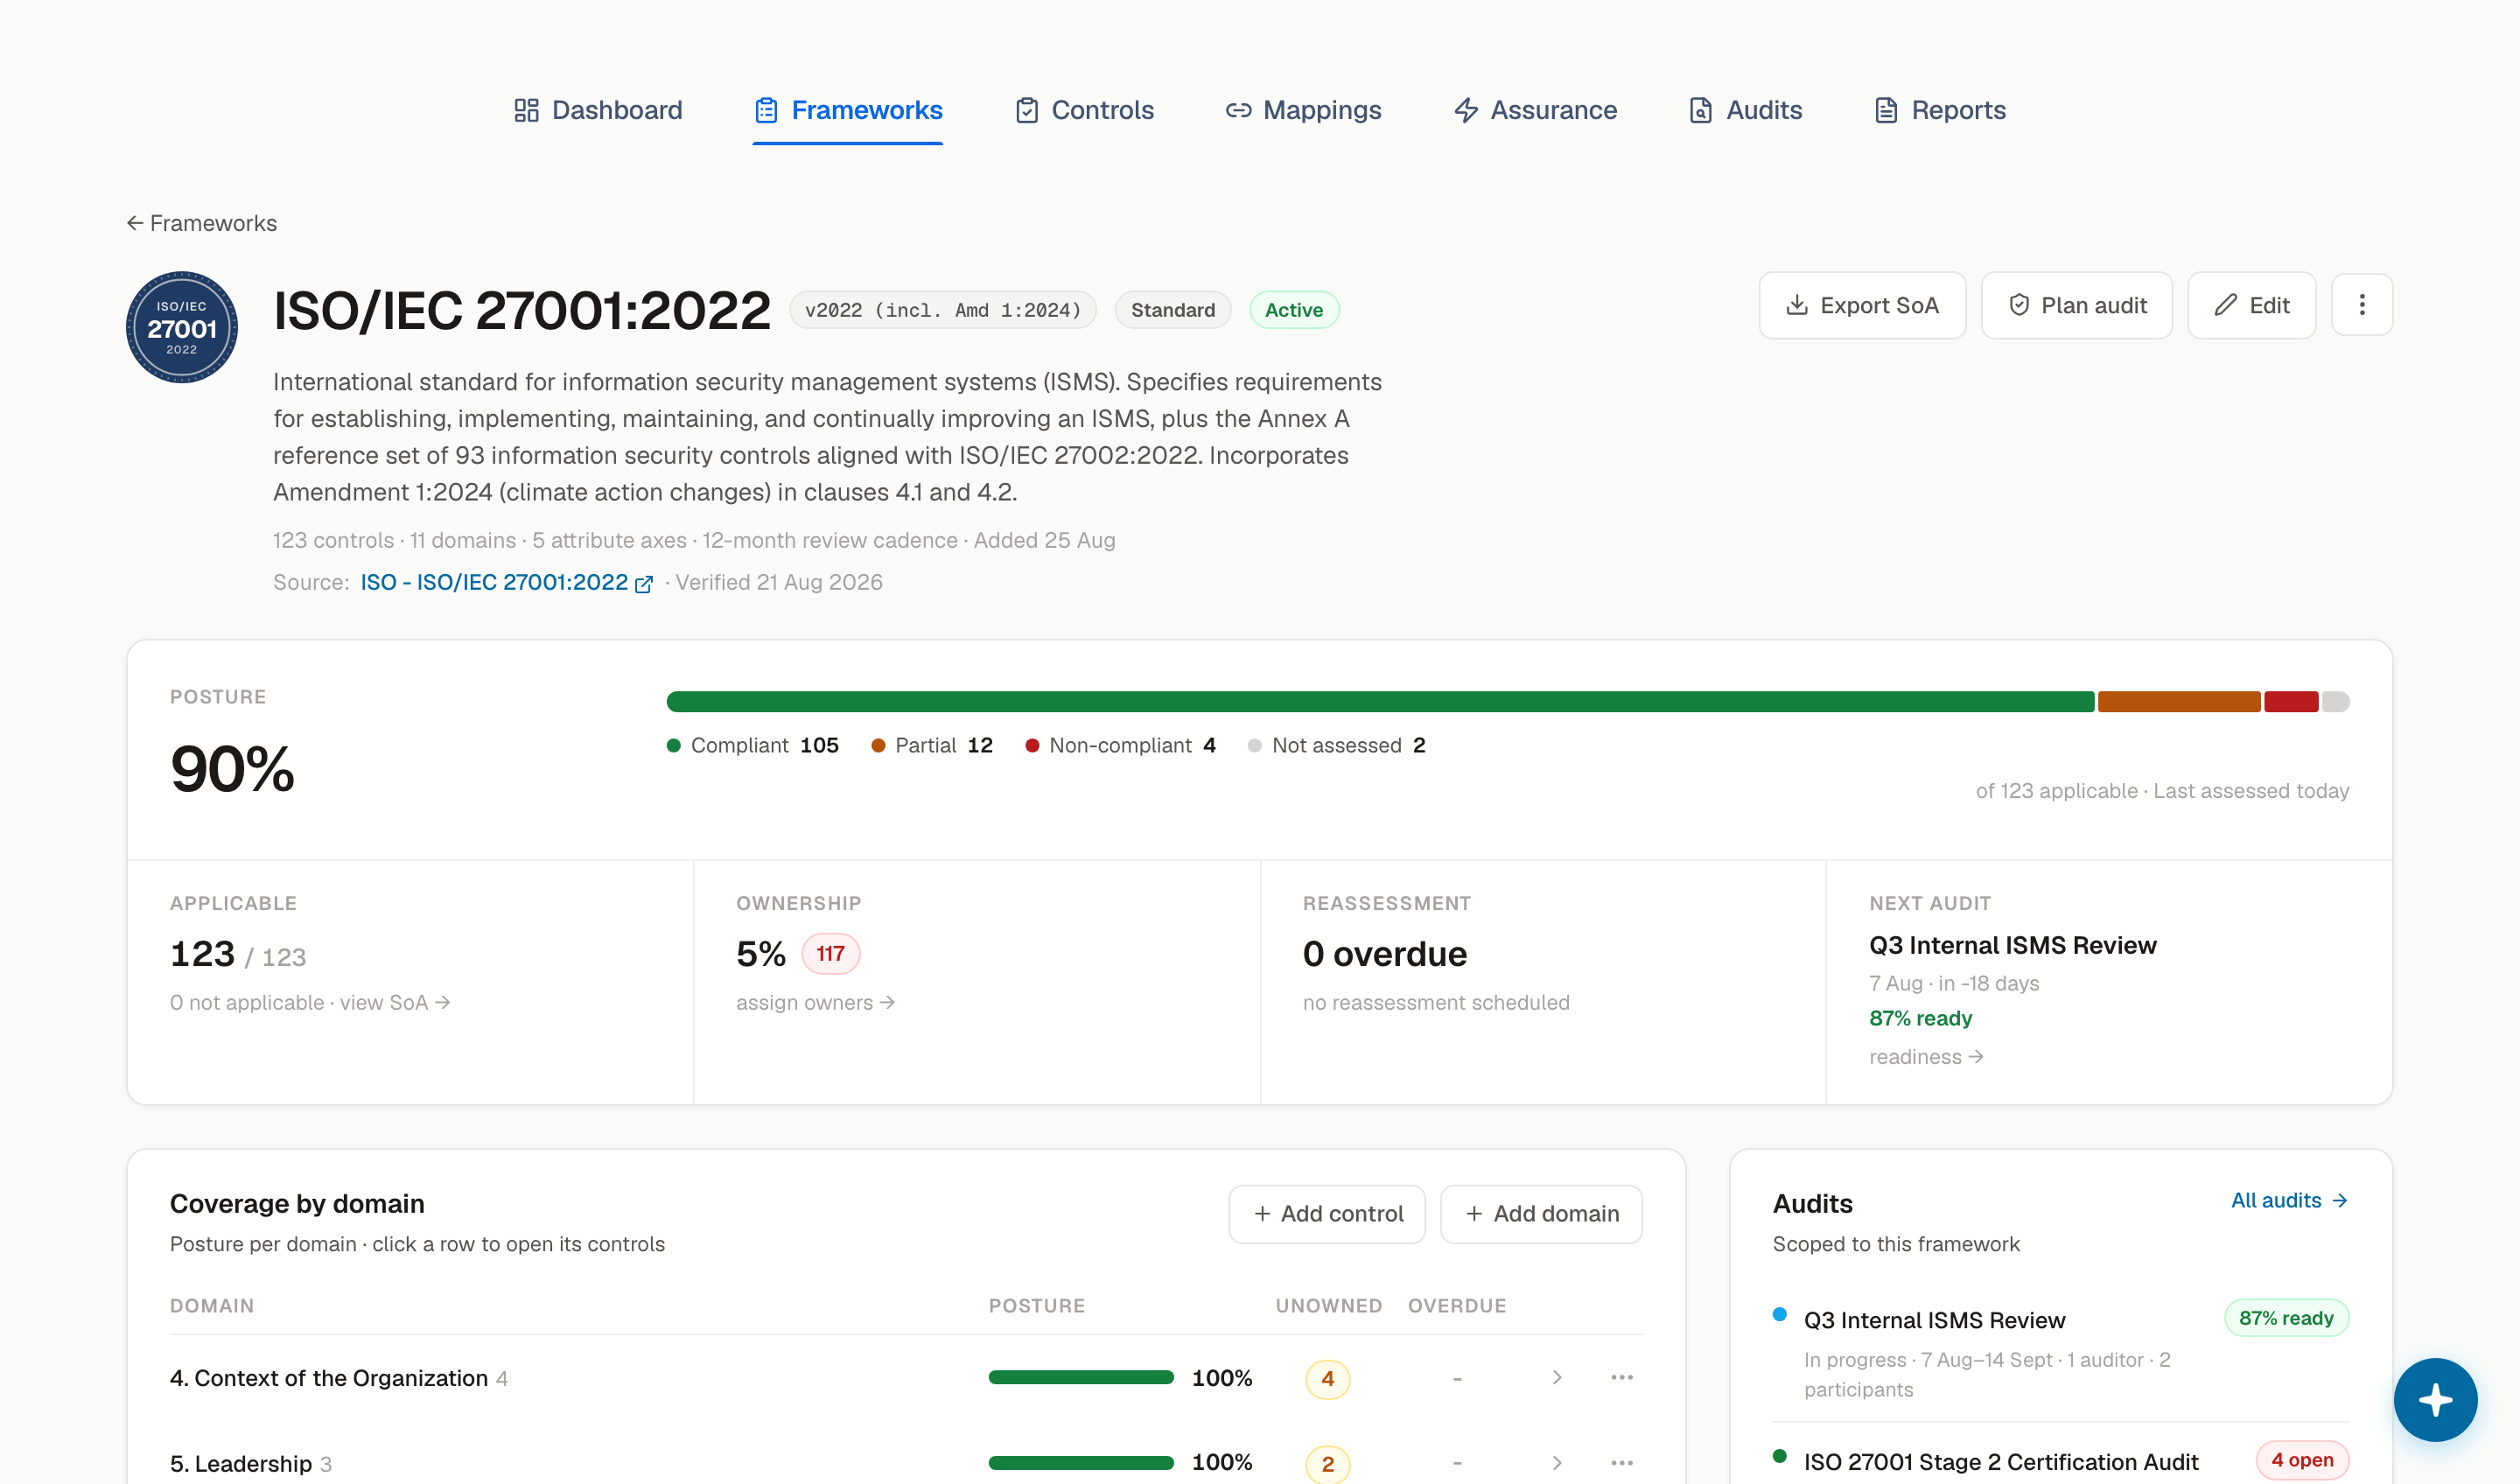
01 · A framework
ISO/IEC 27001:2022 installs with its Annex A controls already worded, not a list of headings for you to fill in. Each one is compliant, partial, non-compliant or not assessed on its own evidence, and posture is counted from those states rather than typed in.

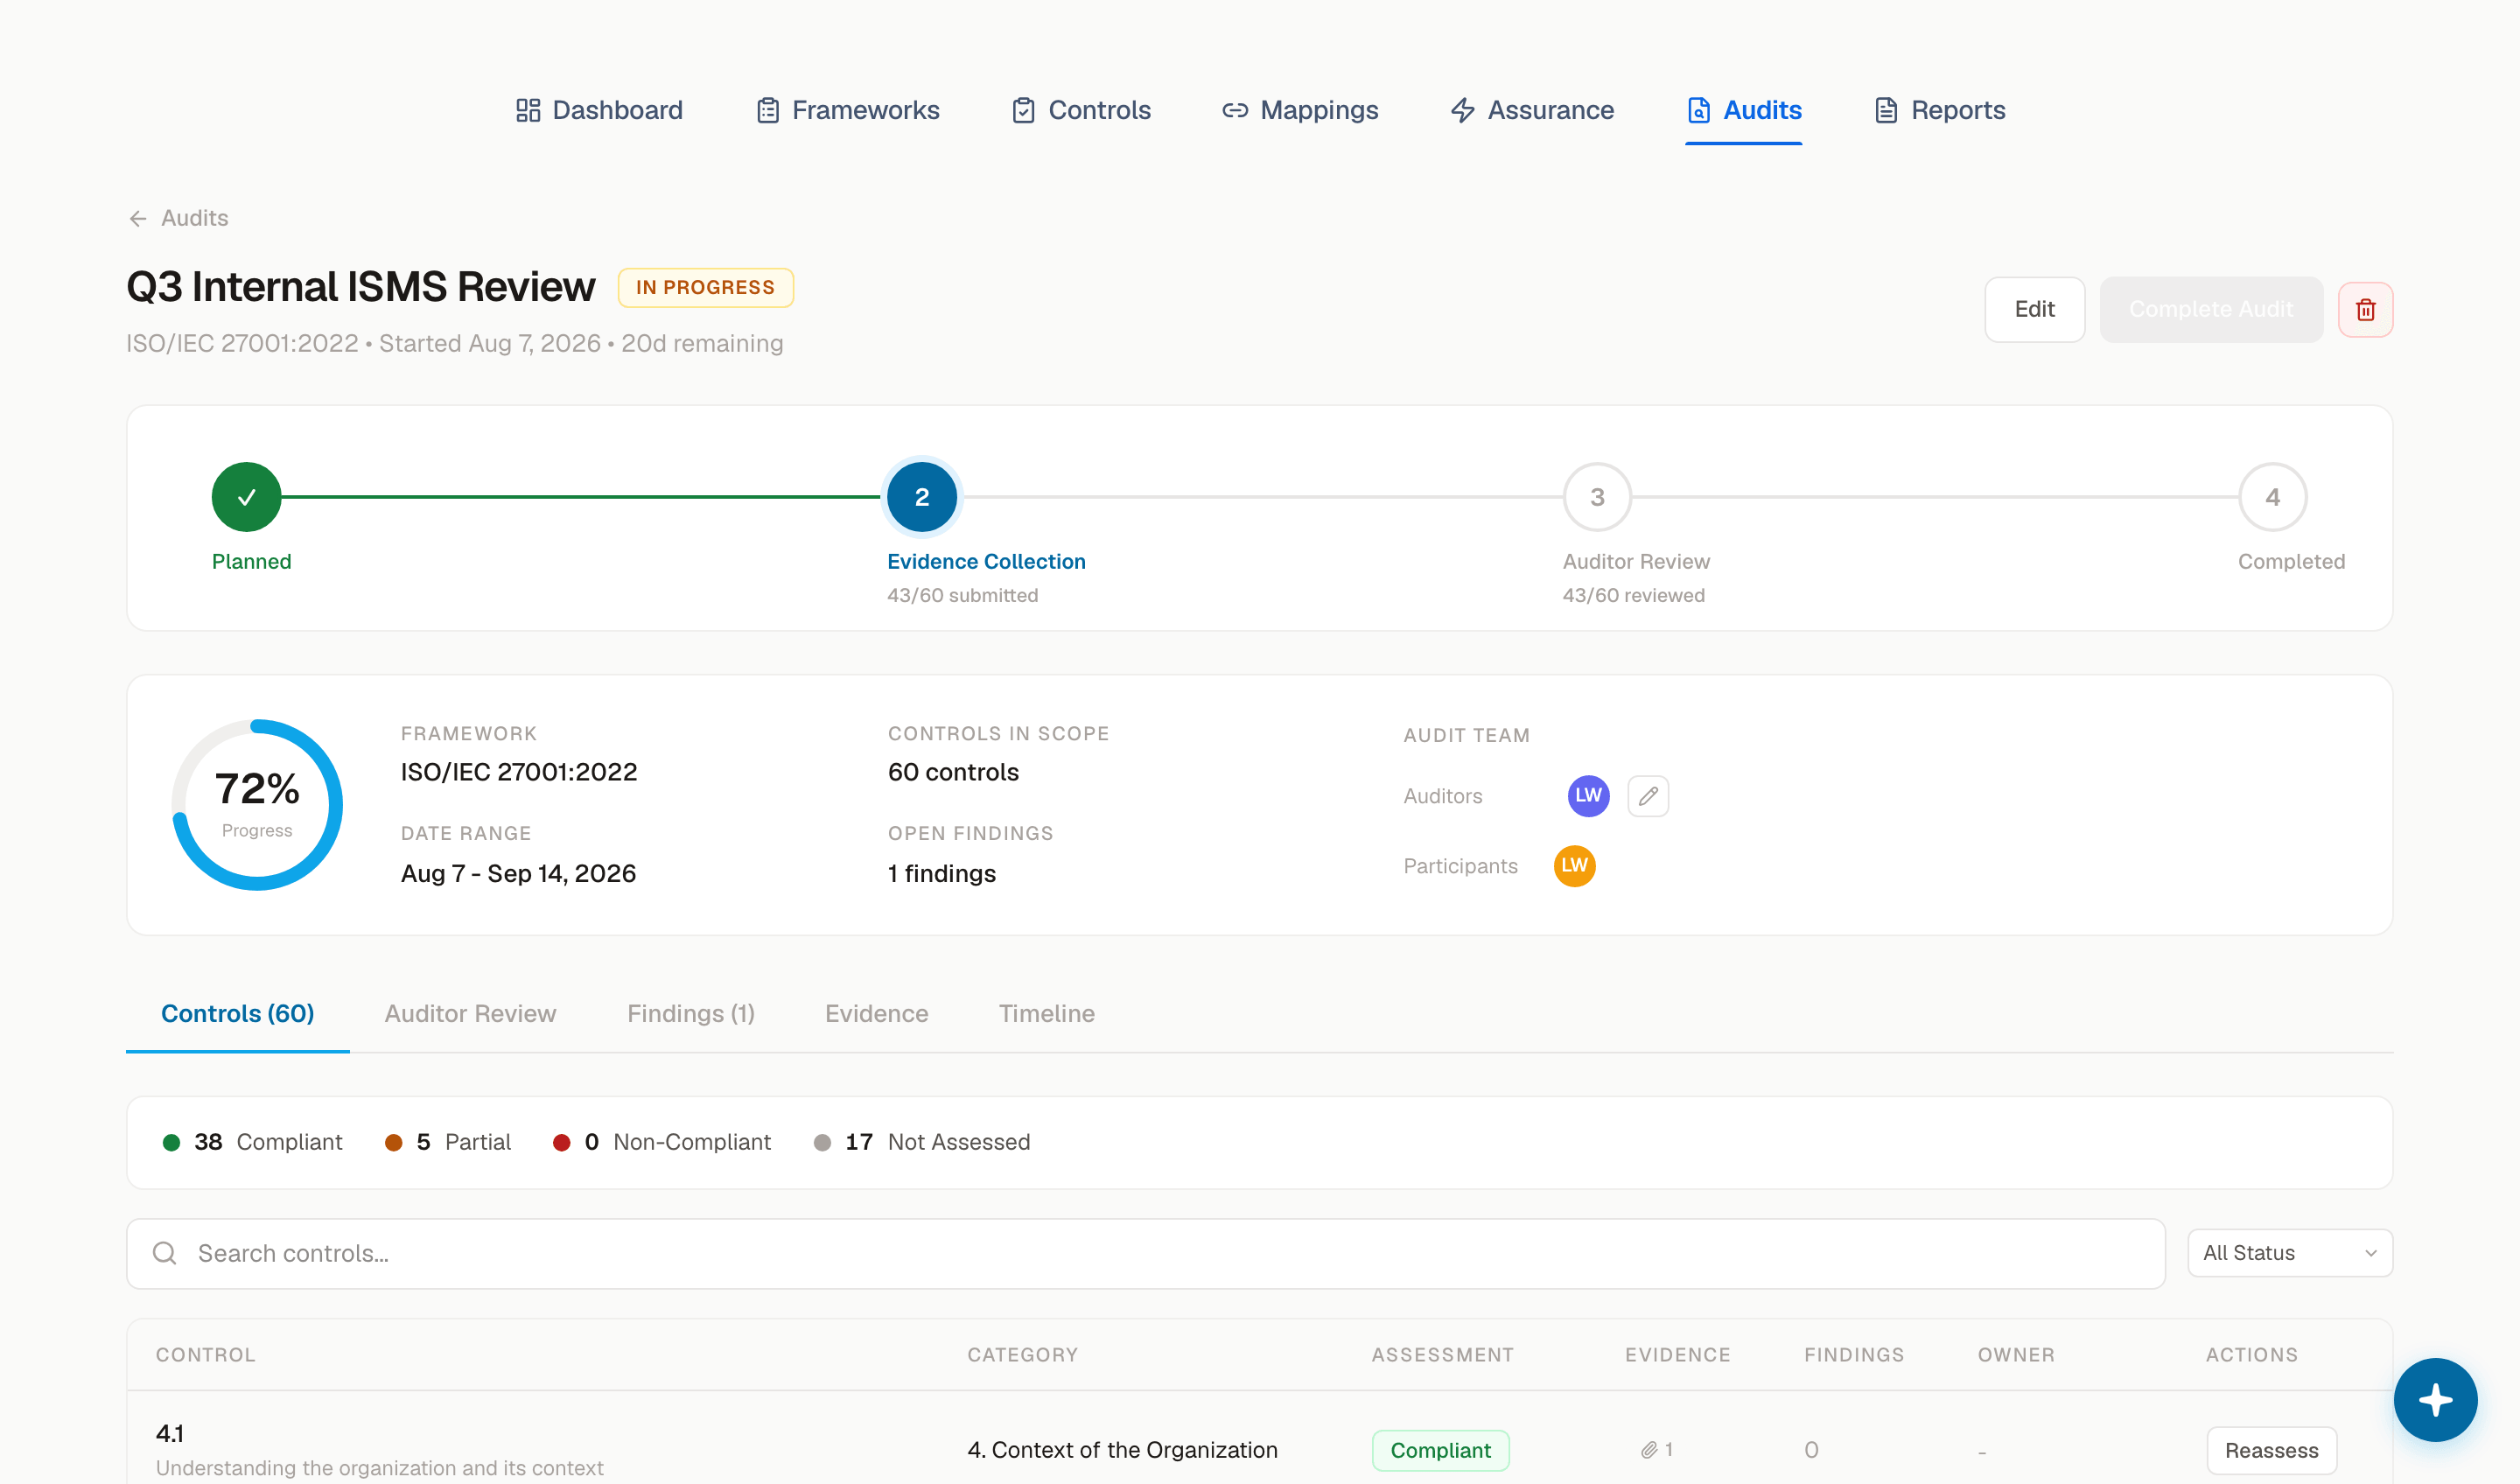
02 · The audit
An audit has a scope, named auditors and an assessment per control. What fails becomes a finding with a severity, an owner and a date, and from there it escalates into the risk register or lands as a remediation task in Security Management.

03 · The posture
Overall posture, days to the next audit, open findings, evidence health and your own queue. Nothing here is a summary someone typed: each tile deep-links to the controls and findings it counted, and the daily snapshots are never back-filled.

Evidence collection
Without Alvor
With Alvor
The audit lifecycle
Every audit follows six structured phases. Alvor guides your team through each with automated workflows and progress tracking.
Define audit scope, objectives, and timeline. Identify stakeholders and confirm framework requirements.
Findings & remediation
Every finding is triaged by severity, linked to its source framework, assigned to an owner, and tracked through remediation. Nothing falls through the cracks.
MFA not enforced on admin accounts
SOC 2 - CC6.1 · J. Park
Encryption key rotation exceeds 90-day policy
PCI DSS - 3.6 · M. Chen
Vendor risk assessments overdue for 3 suppliers
ISO 27001 - A.15.1.1 · S. Nair
Backup restoration test not completed this quarter
NIST CSF - PR.IP-4 · R. Lee
What it replaces
The work in an audit is rarely the assessment. It is finding the evidence again and proving it is still true.
Instead of
A framework as a spreadsheet of headings
A scaffold you have to fill in yourself is a project, not a product.
In Alvor
Packs that install with the official control text, so day one is assessment rather than data entry.
Instead of
Evidence in a shared drive
Screenshots that no longer match the console, and owners who changed role last year.
In Alvor
Evidence uploaded once, linked to every control it satisfies, with a freshness state and a notice before it expires.
Instead of
Findings in a report nobody actions
The audit closes, the document is filed, and the same gap appears next year.
In Alvor
A finding escalates into the risk register or becomes a remediation task with a real owner and a due date.
How it connects
Named precisely, because “everything connects to everything” is not a claim anyone can check. Select any module to see its links.
Links the product makes today
Compliance links to
Further reading
A data centre physical security audit checklist, each item mapped to the PSPF, ISM controls, CIRMP s 11, ISO 27001 A.7 and SOC 2 CC6.4, from site to rack.
What CIRMP section 11 requires of data centre physical security under the SOCI Act, and when the June 2026 enhanced rules can reach a data centre.
What a System Security Plan is, what goes in one, who requires it (NIST 800-171 and CMMC, FedRAMP, FISMA, Australia's ISM and IRAP), how to write one, and why most SSPs are out of date the day they are signed.
Compliance
Alvor maps your controls once and satisfies every framework automatically. Evidence is collected continuously from your existing tools - so when the auditor arrives, you answer in minutes, not weeks.