The Platform

One platform that connects
your entire security program

Most teams juggle a dozen disconnected tools. Alvor replaces the stack with a single system where assets, risks, policies, and evidence are connected by default.

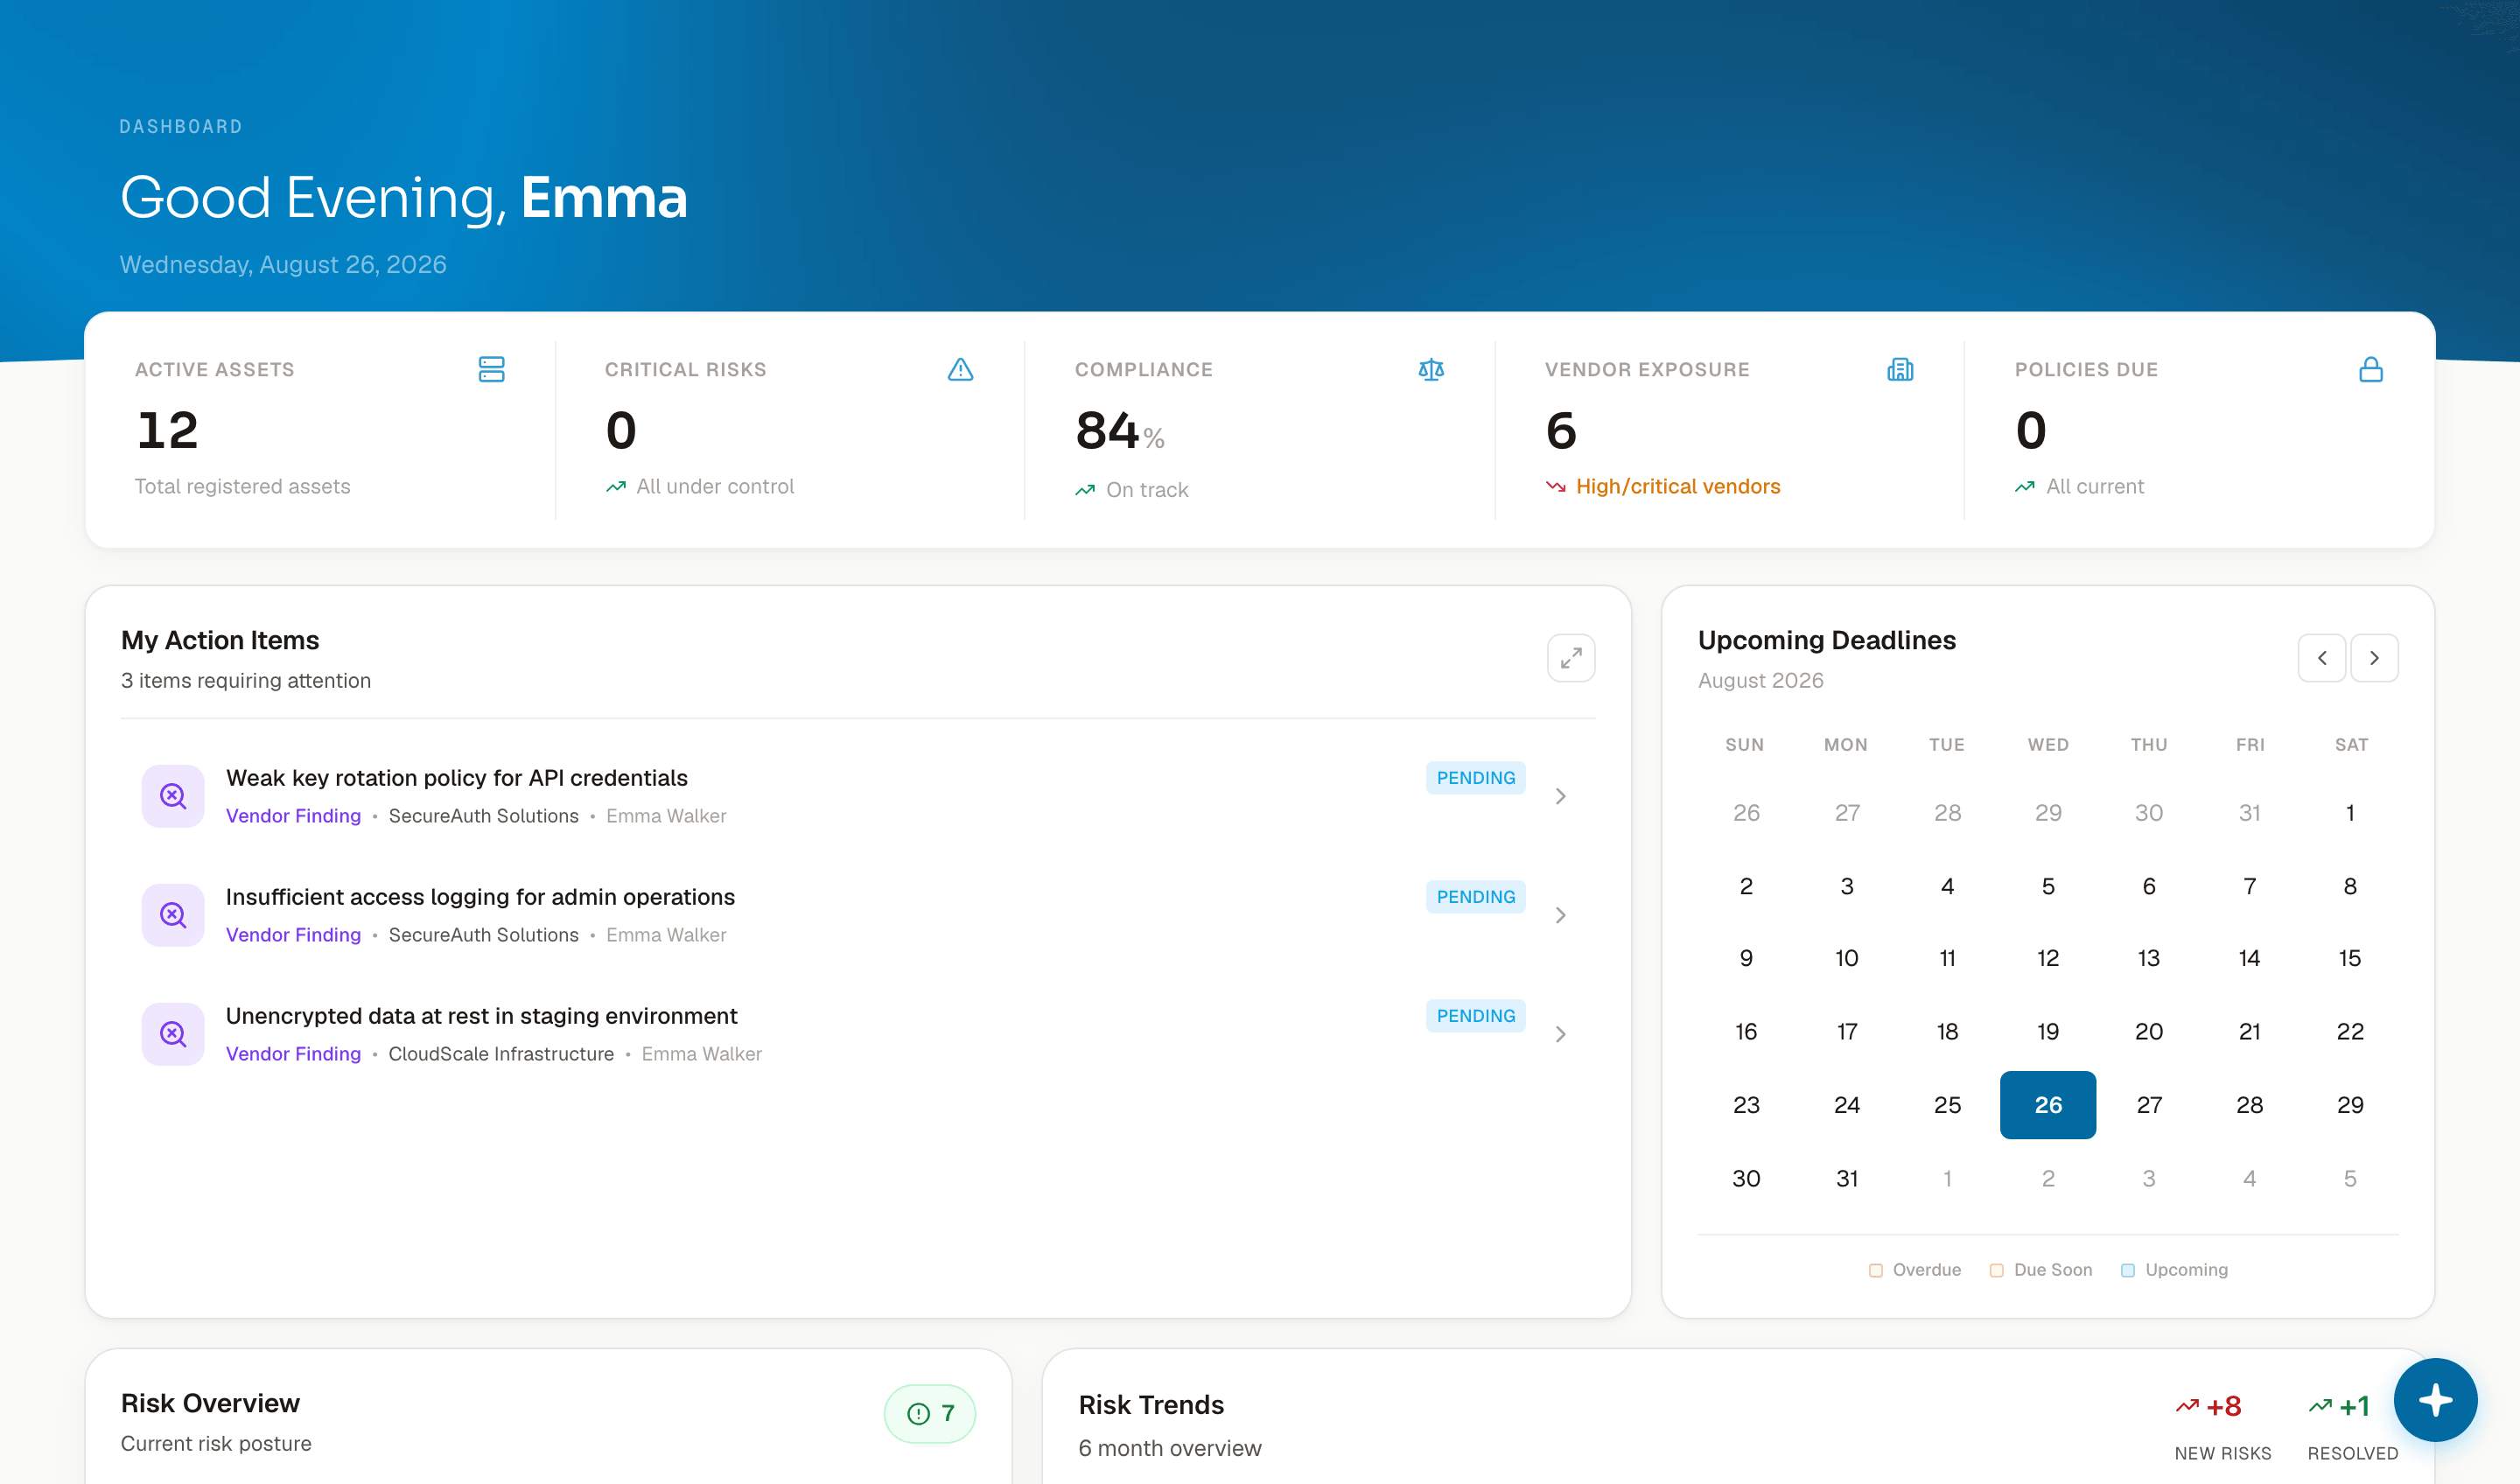
app.alvor.io/dashboard
The Alvor platform dashboard: posture tiles, action items, and deadlines in one view

Eight modules on one set of data, in the order a program uses them

The modules share one set of data, with named links between them. Select a module to see the links it makes today.

01Set the program
02Design new systems
03Prove controls work
04Manage risk, vendors and continuity
RegisterThe register the rest stands on
Runs onYour own instance
Dedicated cloudOne instance for your company, in your region
On-premiseThe same platform, on your own servers
Air-gappedFully disconnected, with a self-hosted model

Links the product makes today

Select a module above

Each module lists the records it shares with the others: a compliance finding that escalates into a risk, a design sign-off that raises one, an asset every risk can name. Only links the product makes today are shown.

Eight modules, one system of record.

Real screens from the product: one data model underneath, a module for each part of the program.

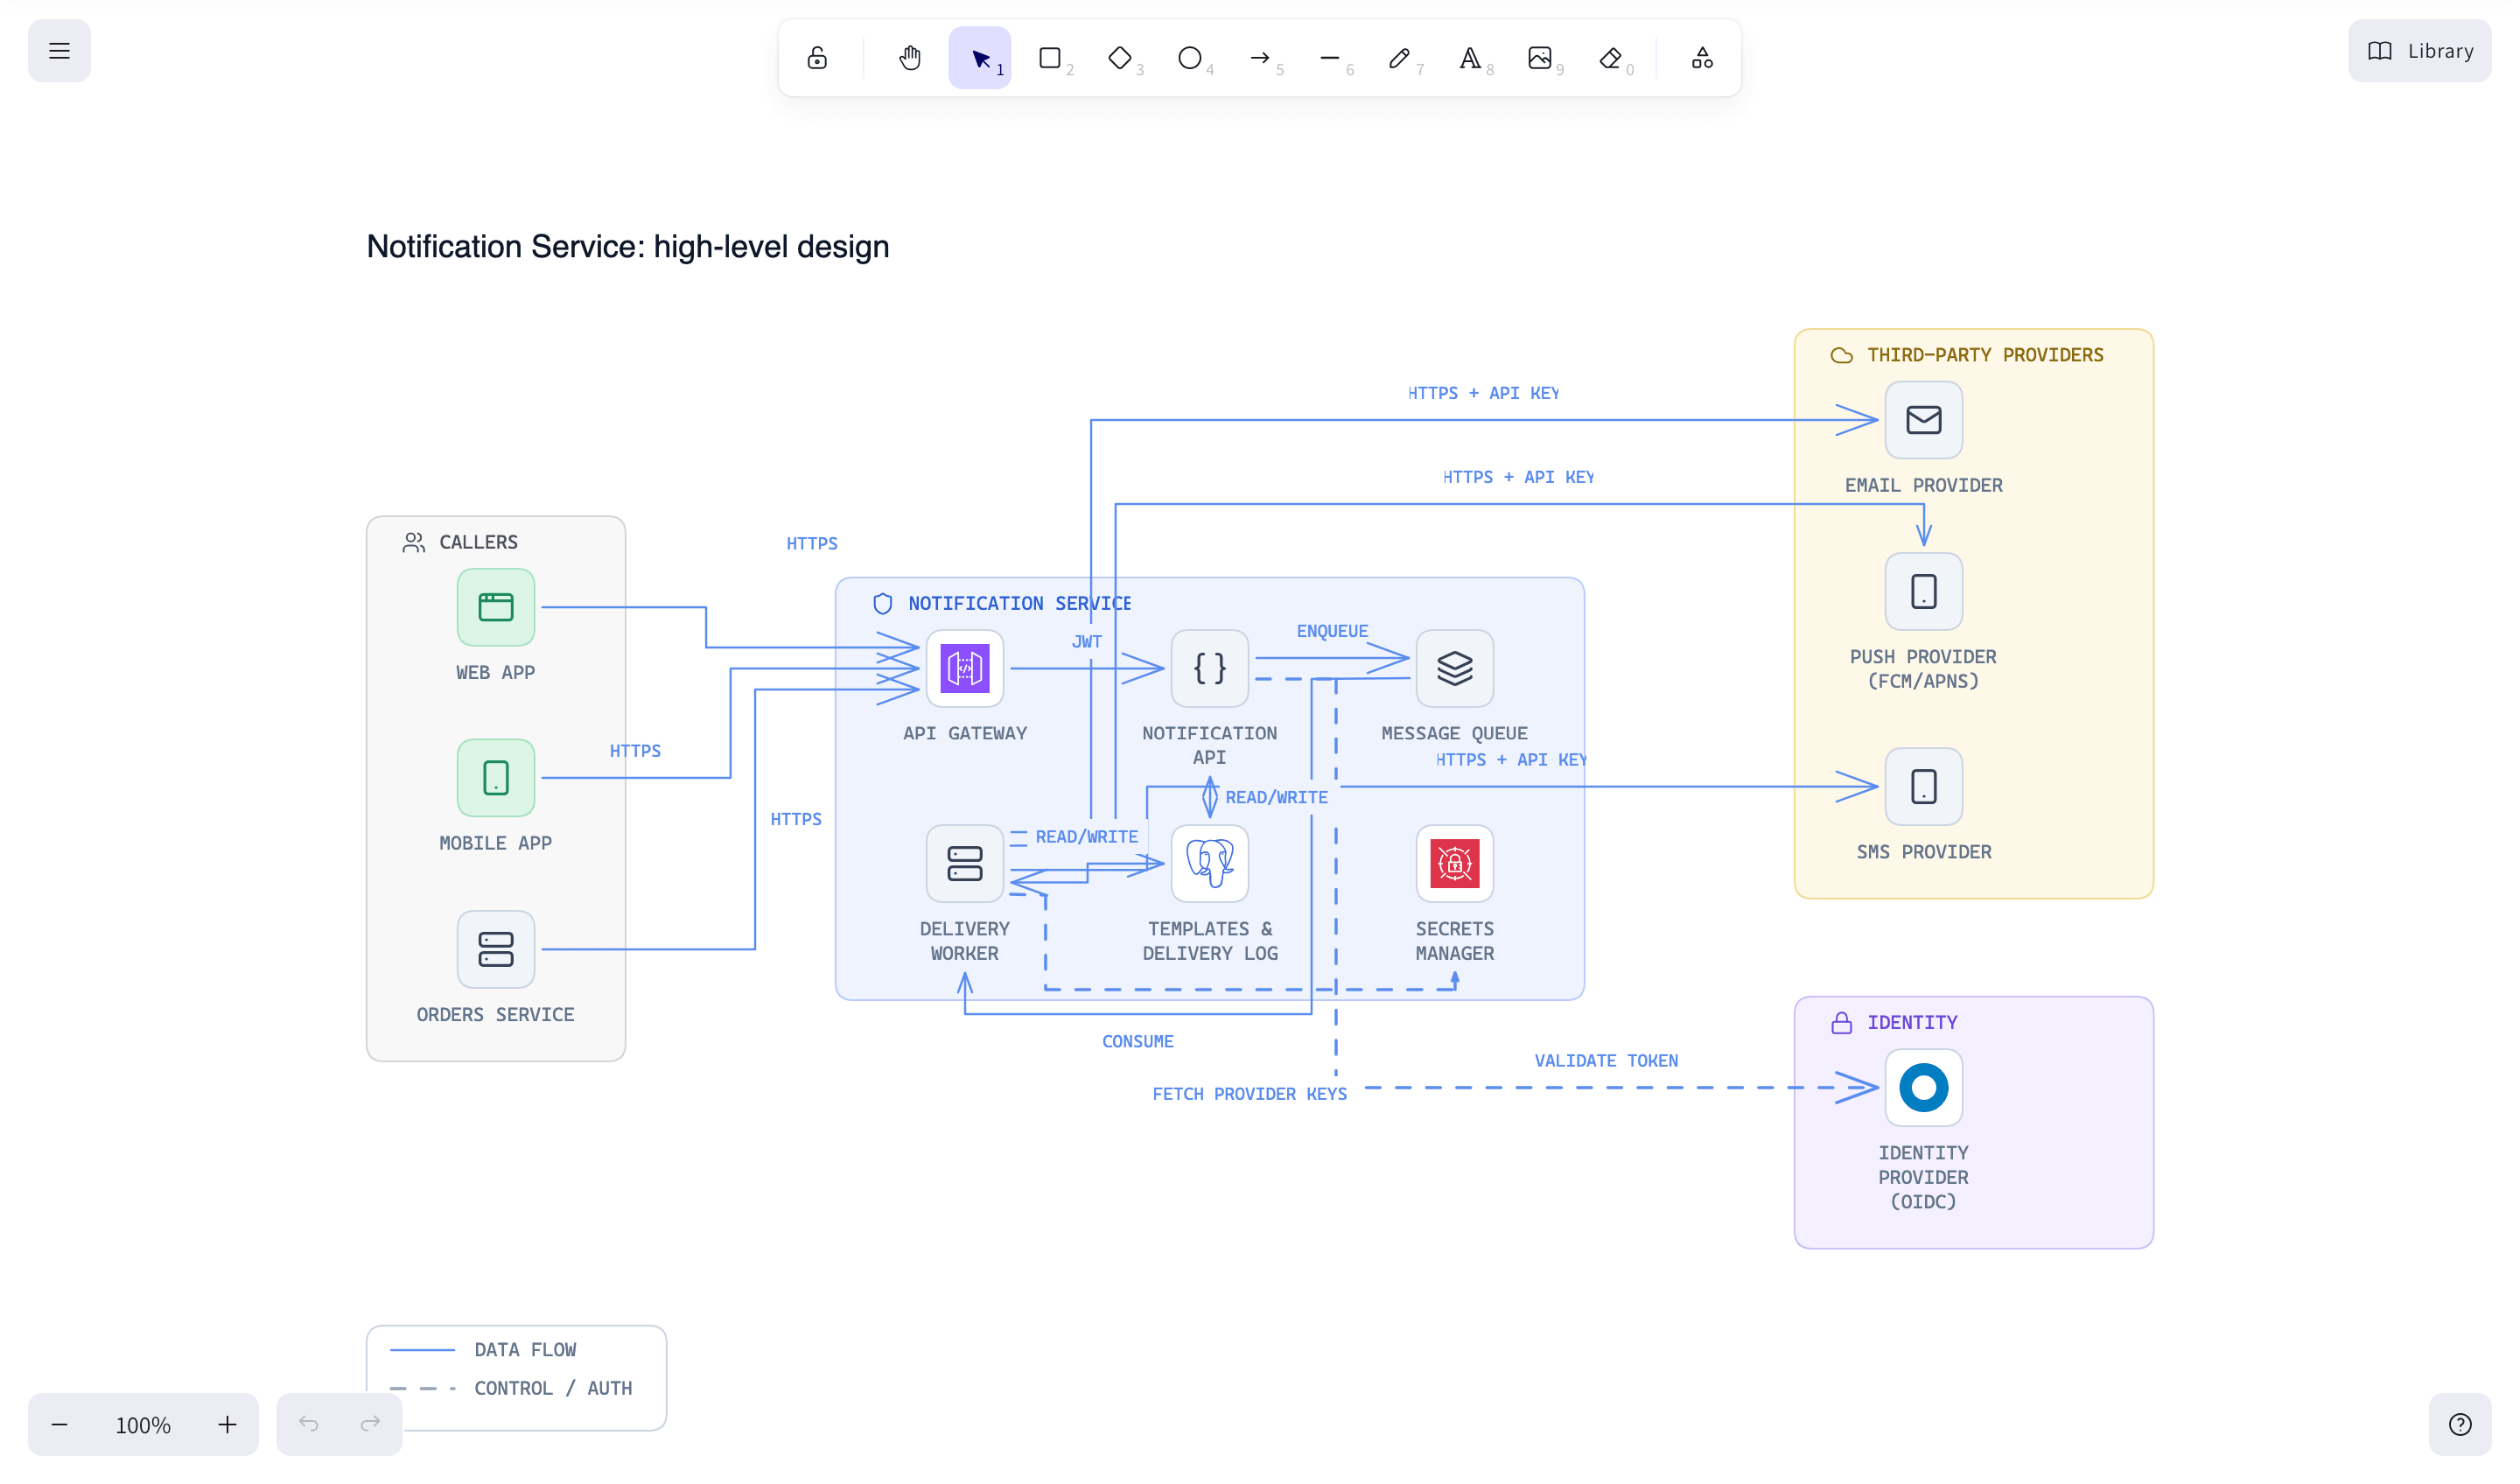
Draw your architecture, run STRIDE threat models on the live diagram, and map the controls that answer each threat. Named people sign the design off, and the record keeps who approved it and when.

STRIDE threat modelsThreat-driven controlsNamed sign-offs
Explore Secure by Design
app.alvor.io/secure-by-design
The Secure by Design canvas: an architecture diagram with trust boundaries and mapped controls

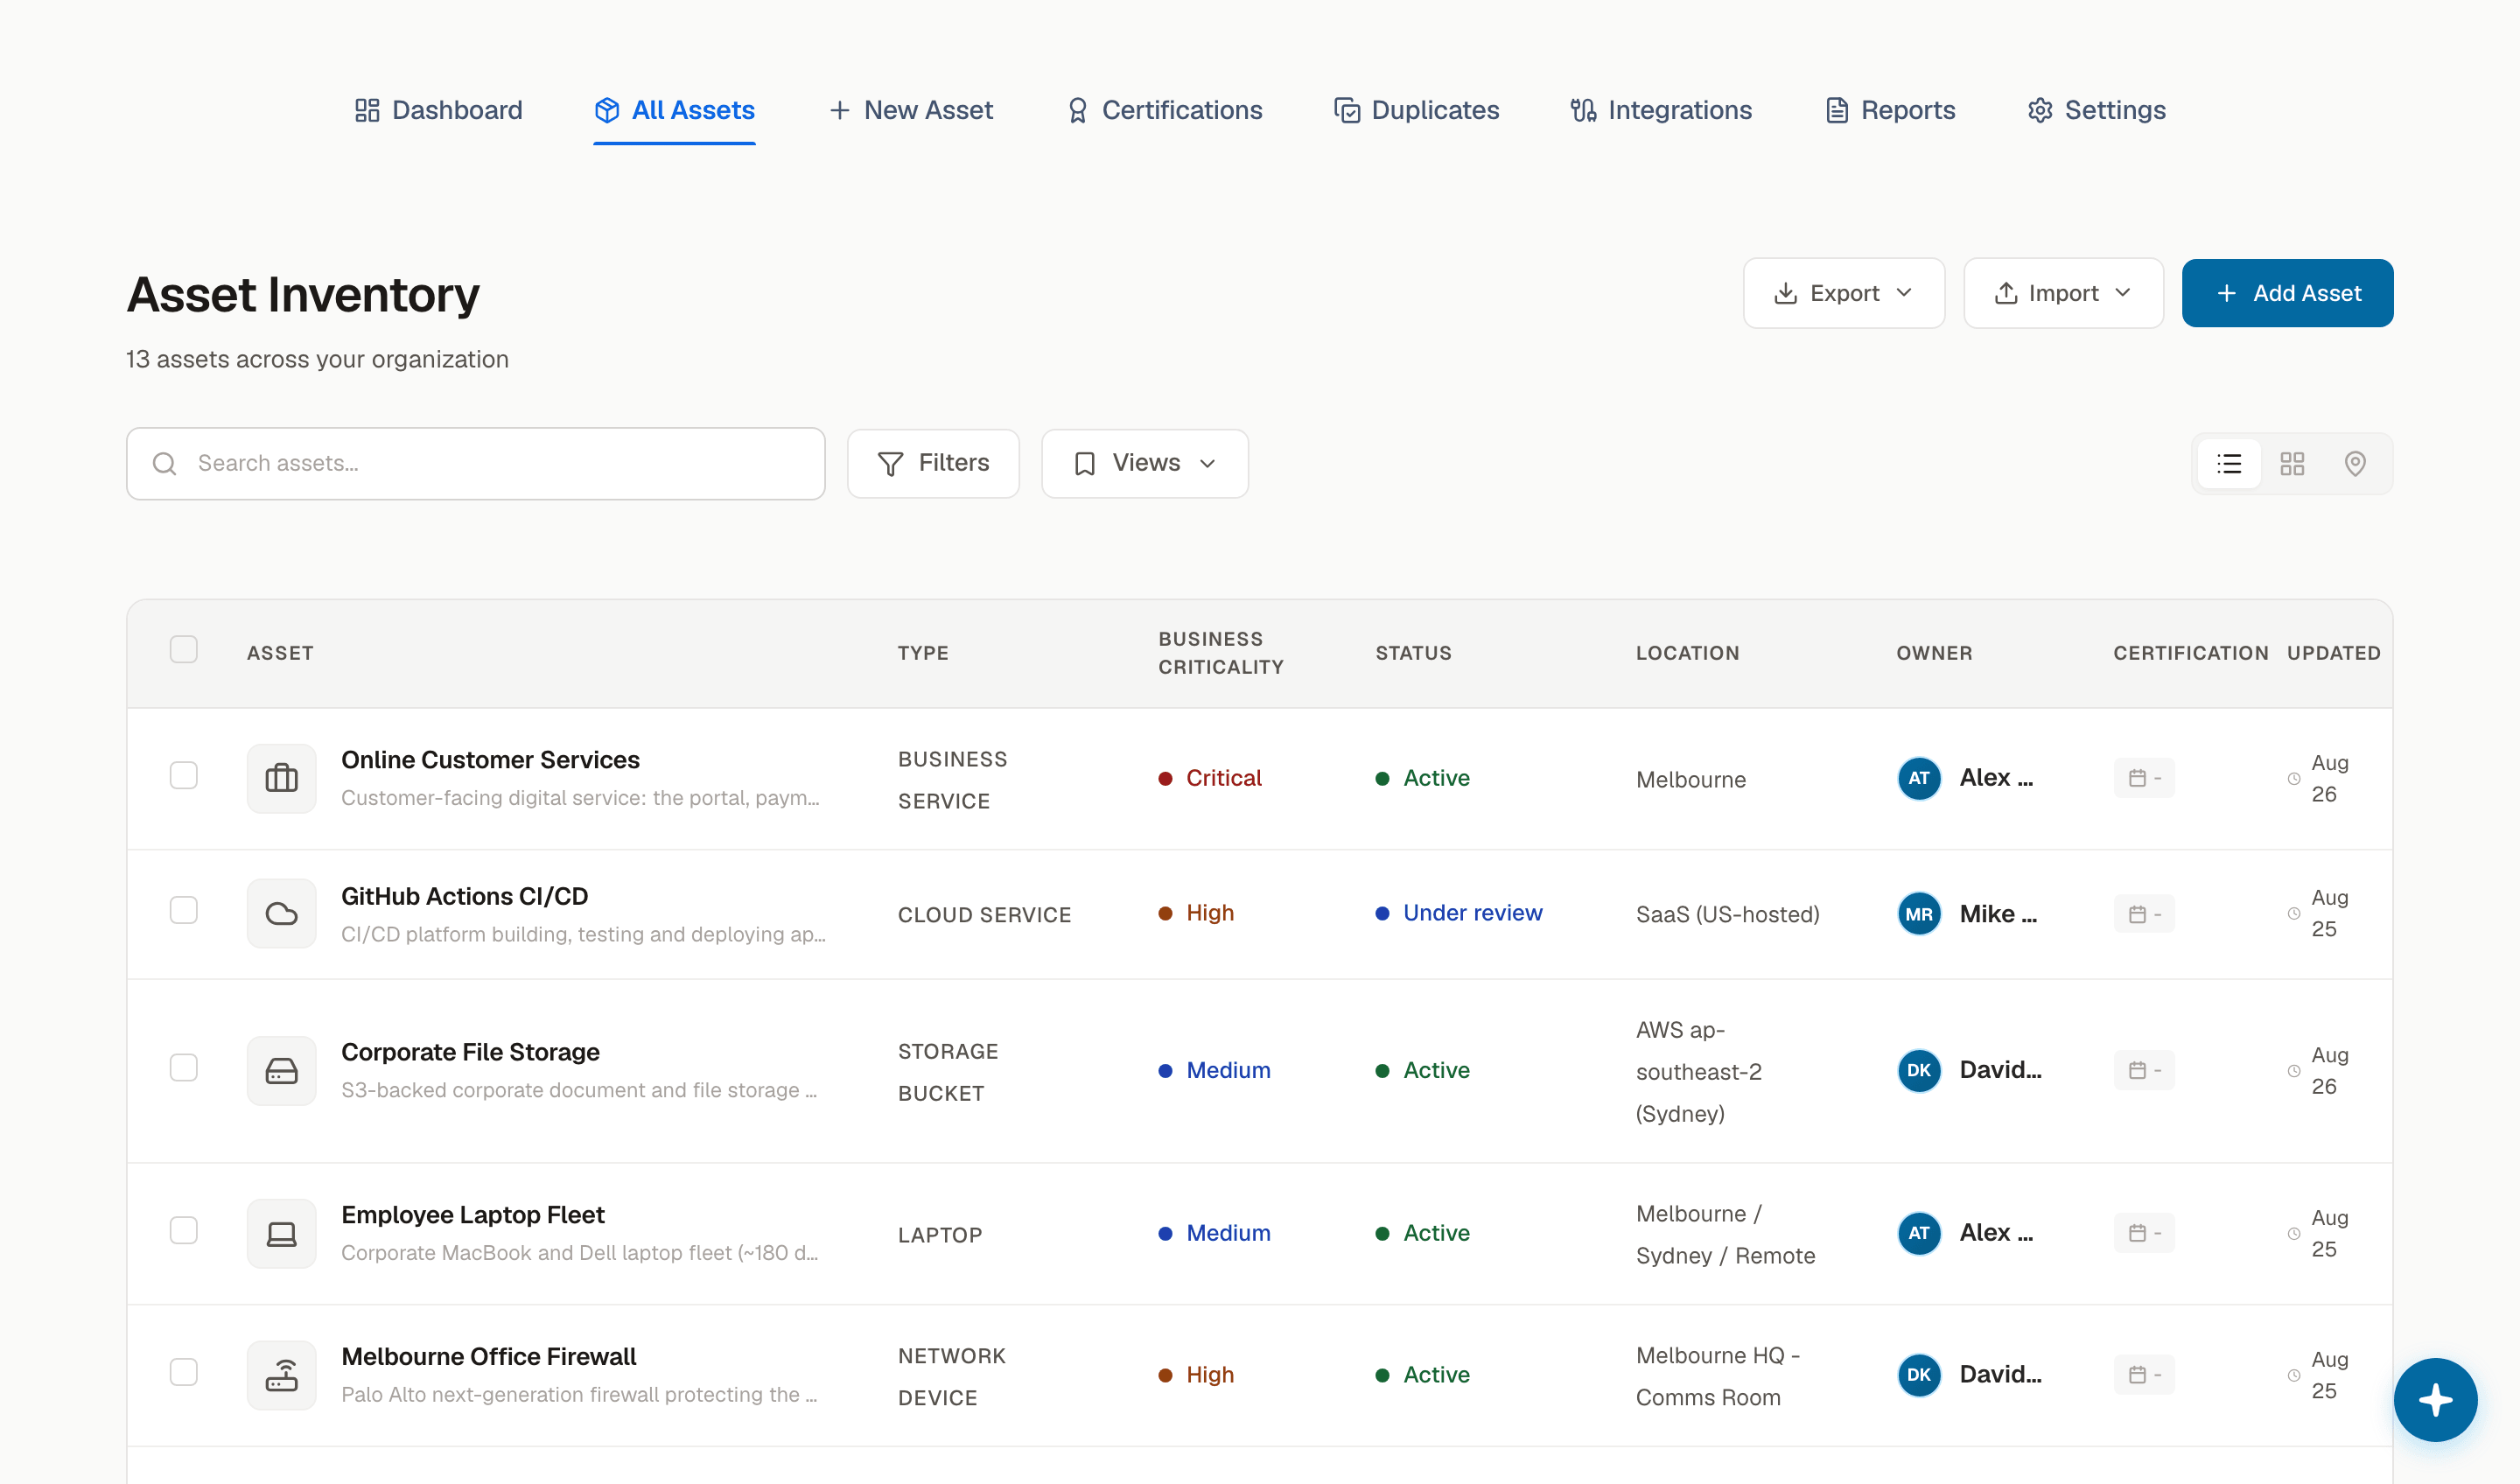
A register built for security: systems, data, vendors and the people who own them, connected to the risks they carry and the plans that recover them, and filled automatically from the tools you already run.

An owner on every assetLinked to risks and plansFilled by your tools
Explore Asset Management
app.alvor.io/assets
The asset register listing systems with owners, classifications, and relationships

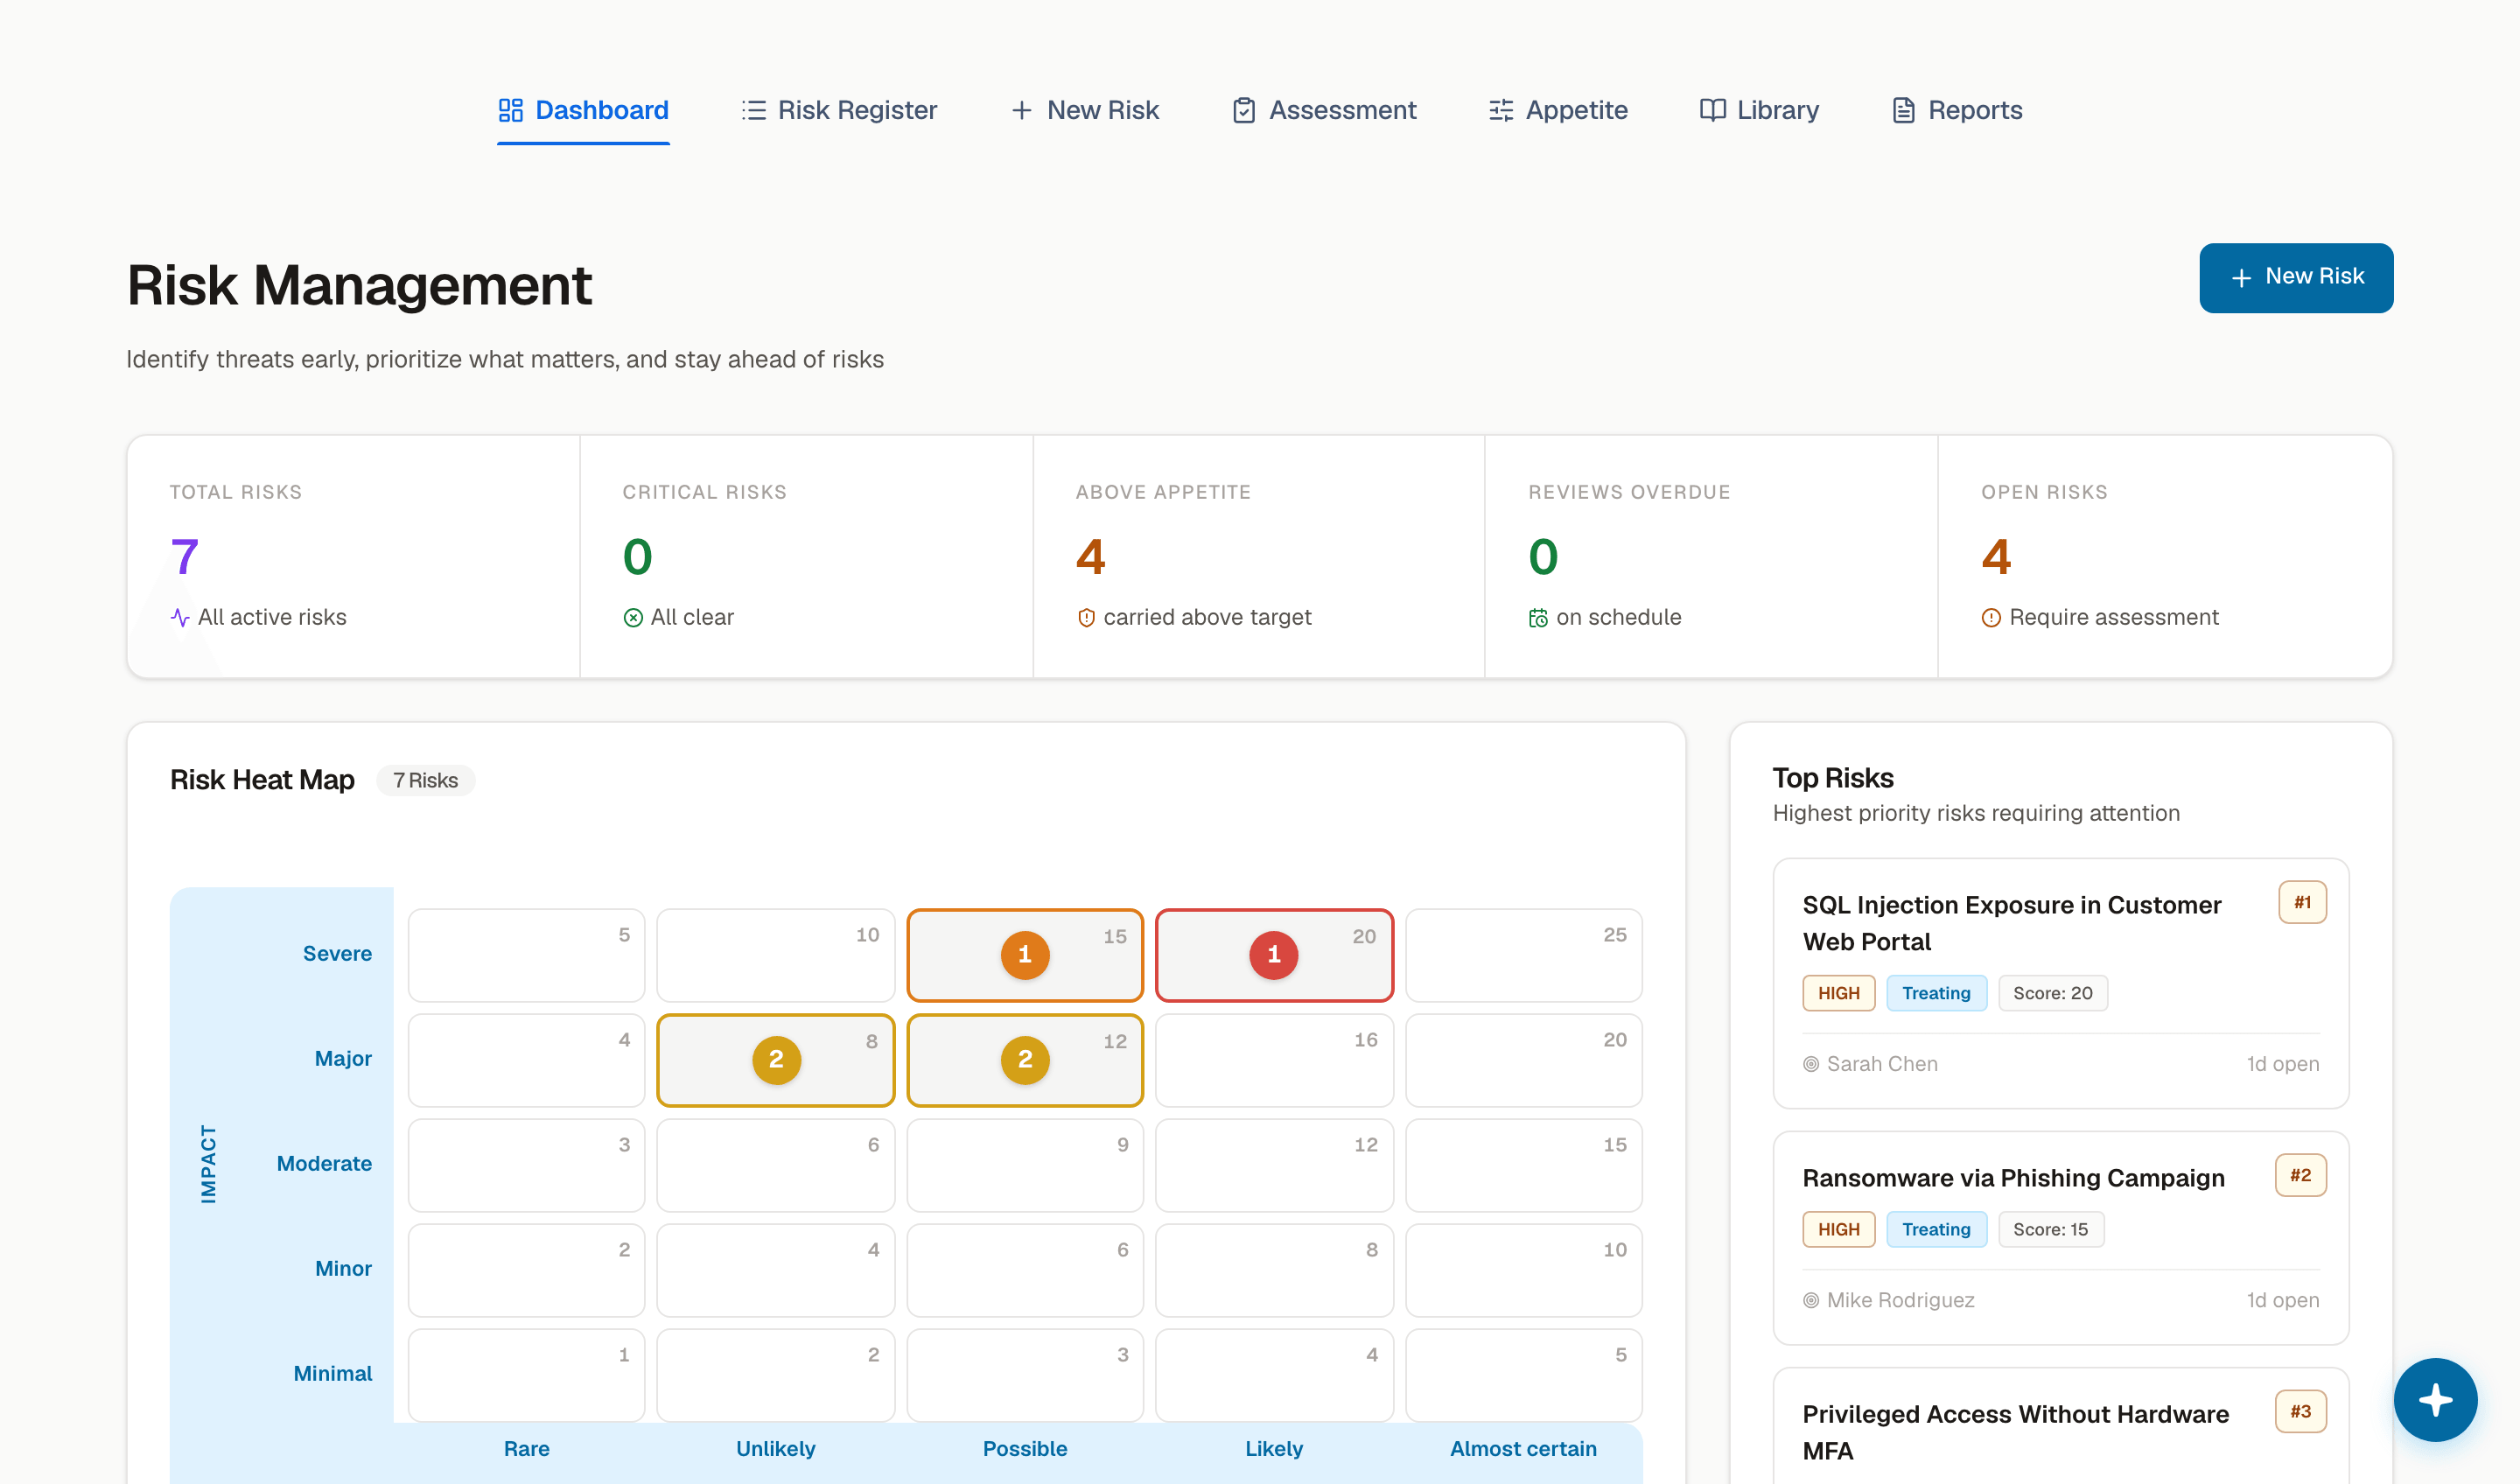
A register with owners, treatment, and appetite thresholds. Risks link to the assets they touch and the controls that mitigate them, so posture is an answer, not an argument.

Owners & treatmentAppetite thresholdsLinked to controls
Explore Risk Management
app.alvor.io/risk
The risk dashboard with posture, trends, and the risk register

Frameworks that install with their official control text, and crosswalks built from NIST's public informative references. Attach evidence to a control once and reuse it across ISO 27001, NIST, and every framework you run.

Verbatim control textEvidence reused everywhereCrosswalks from NIST
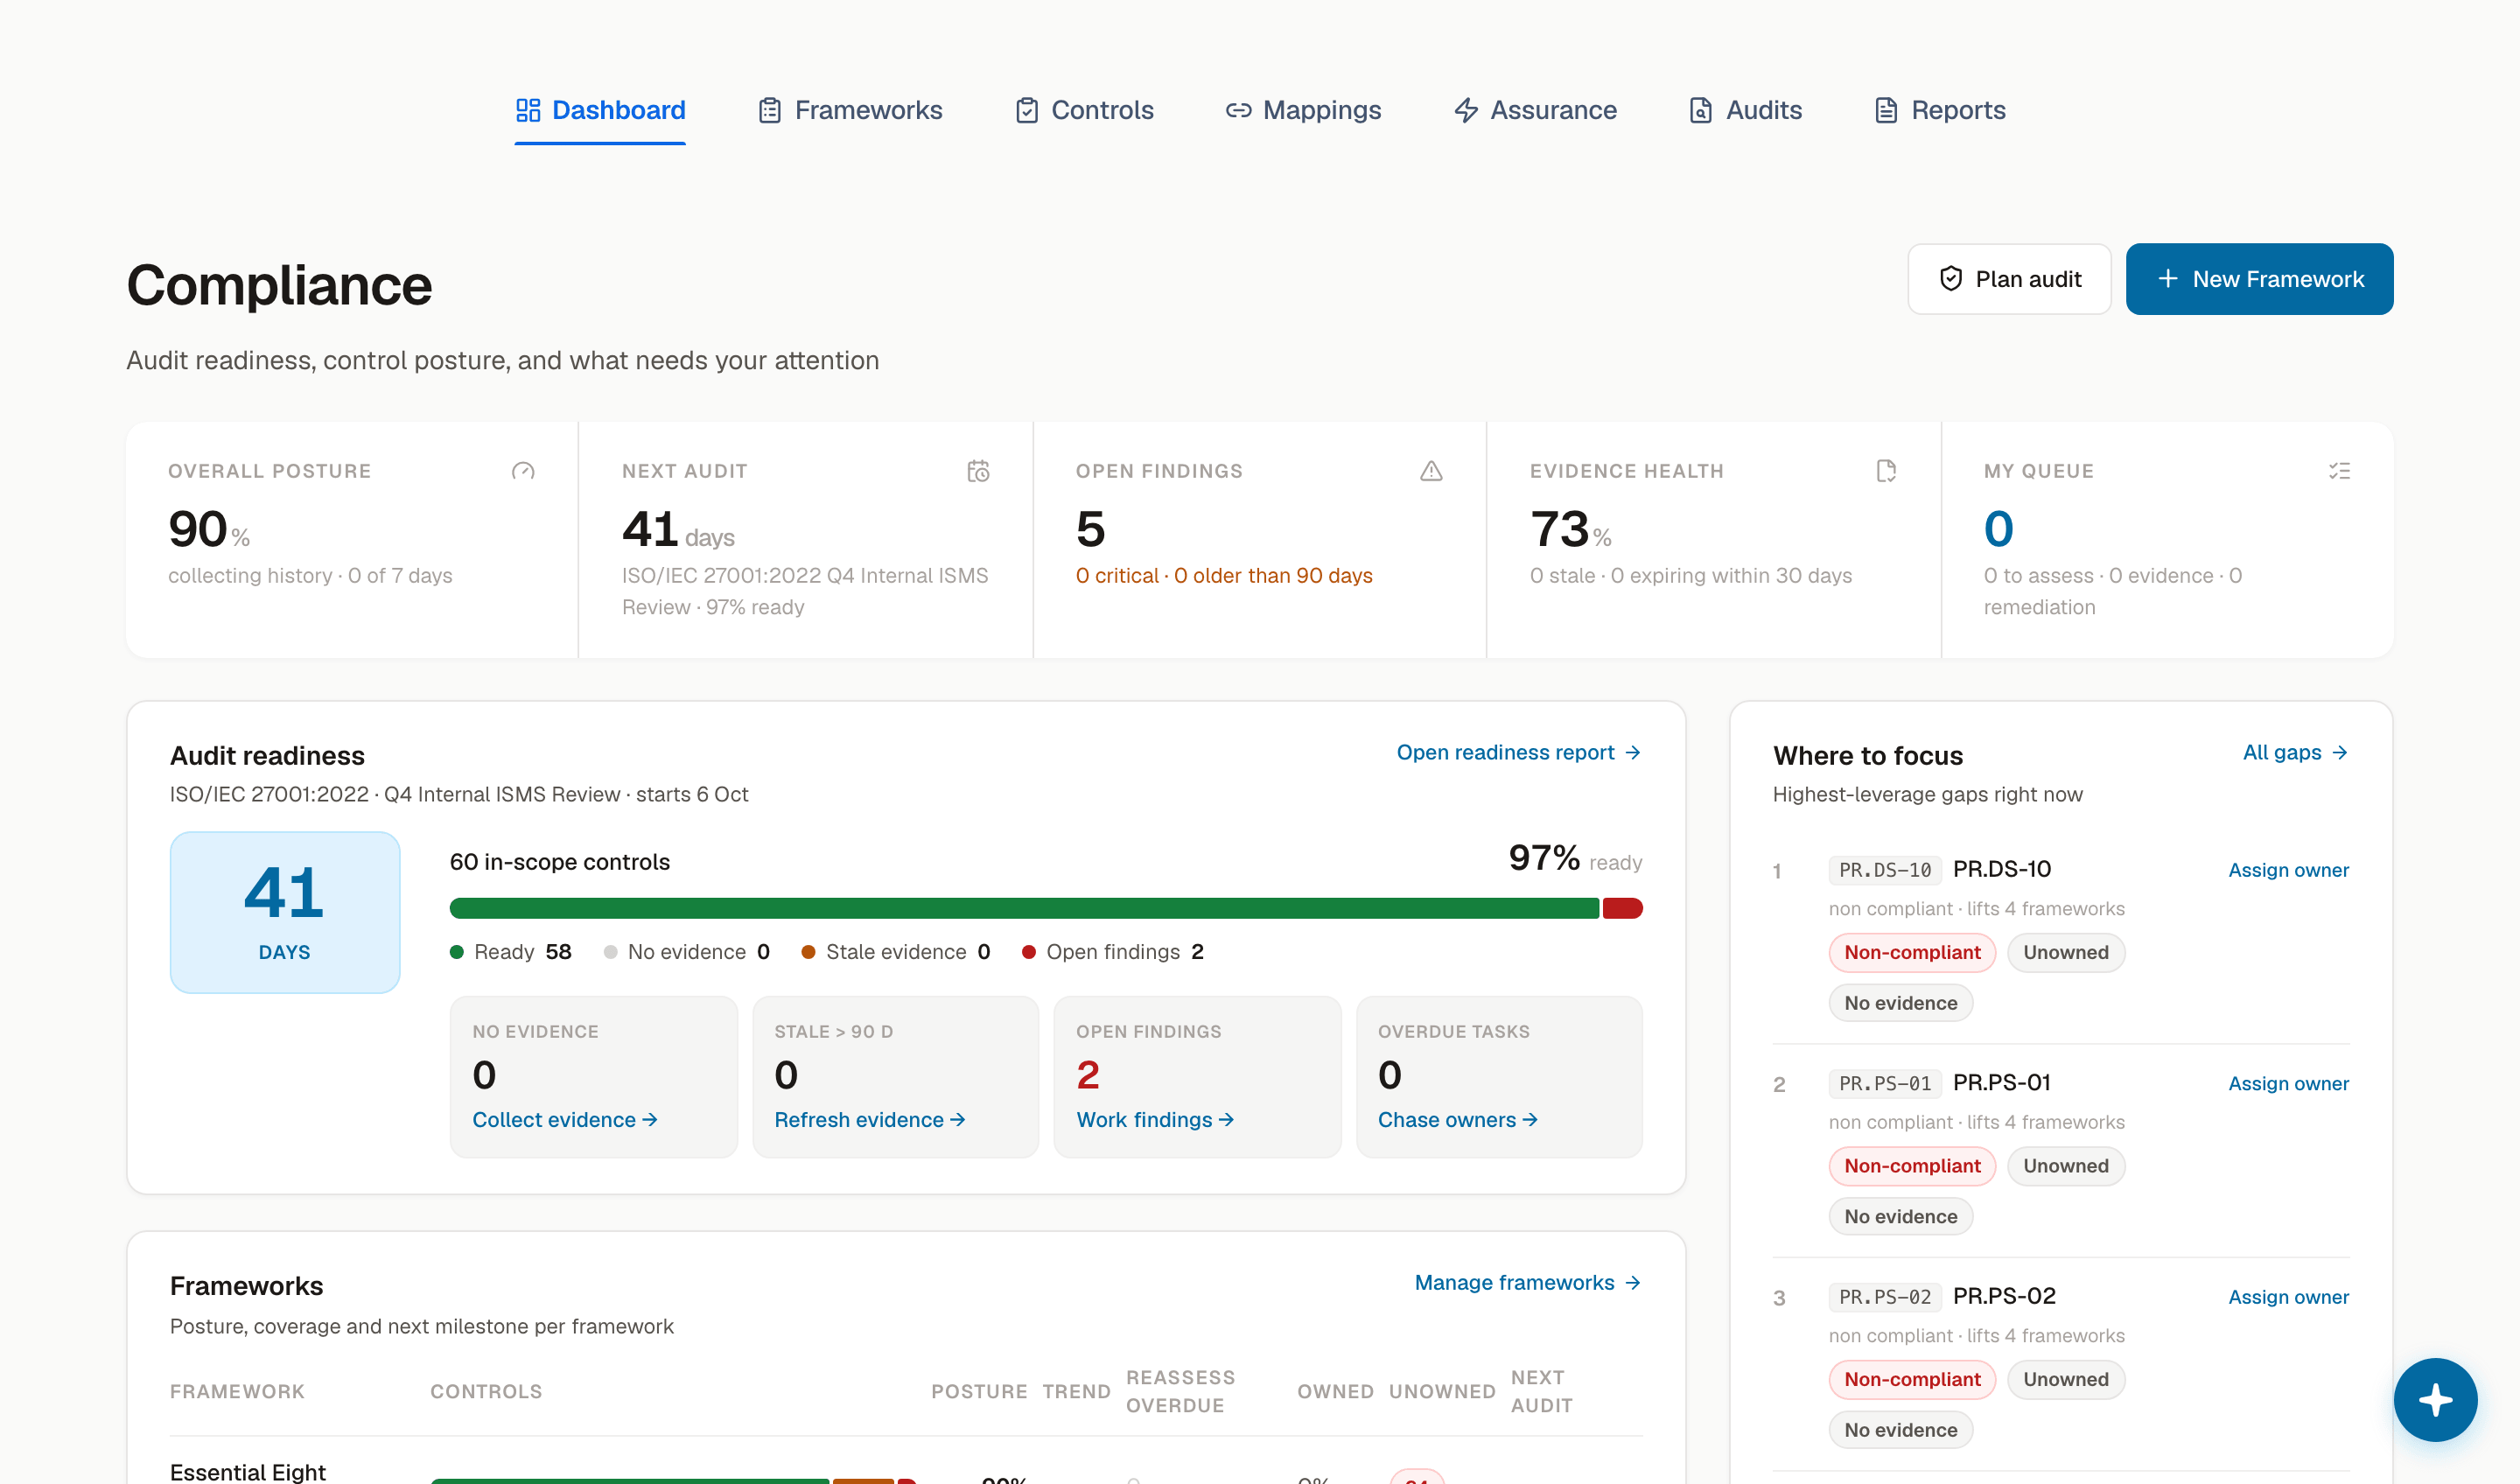
Explore Compliance
app.alvor.io/compliance
The compliance dashboard with framework posture and control status

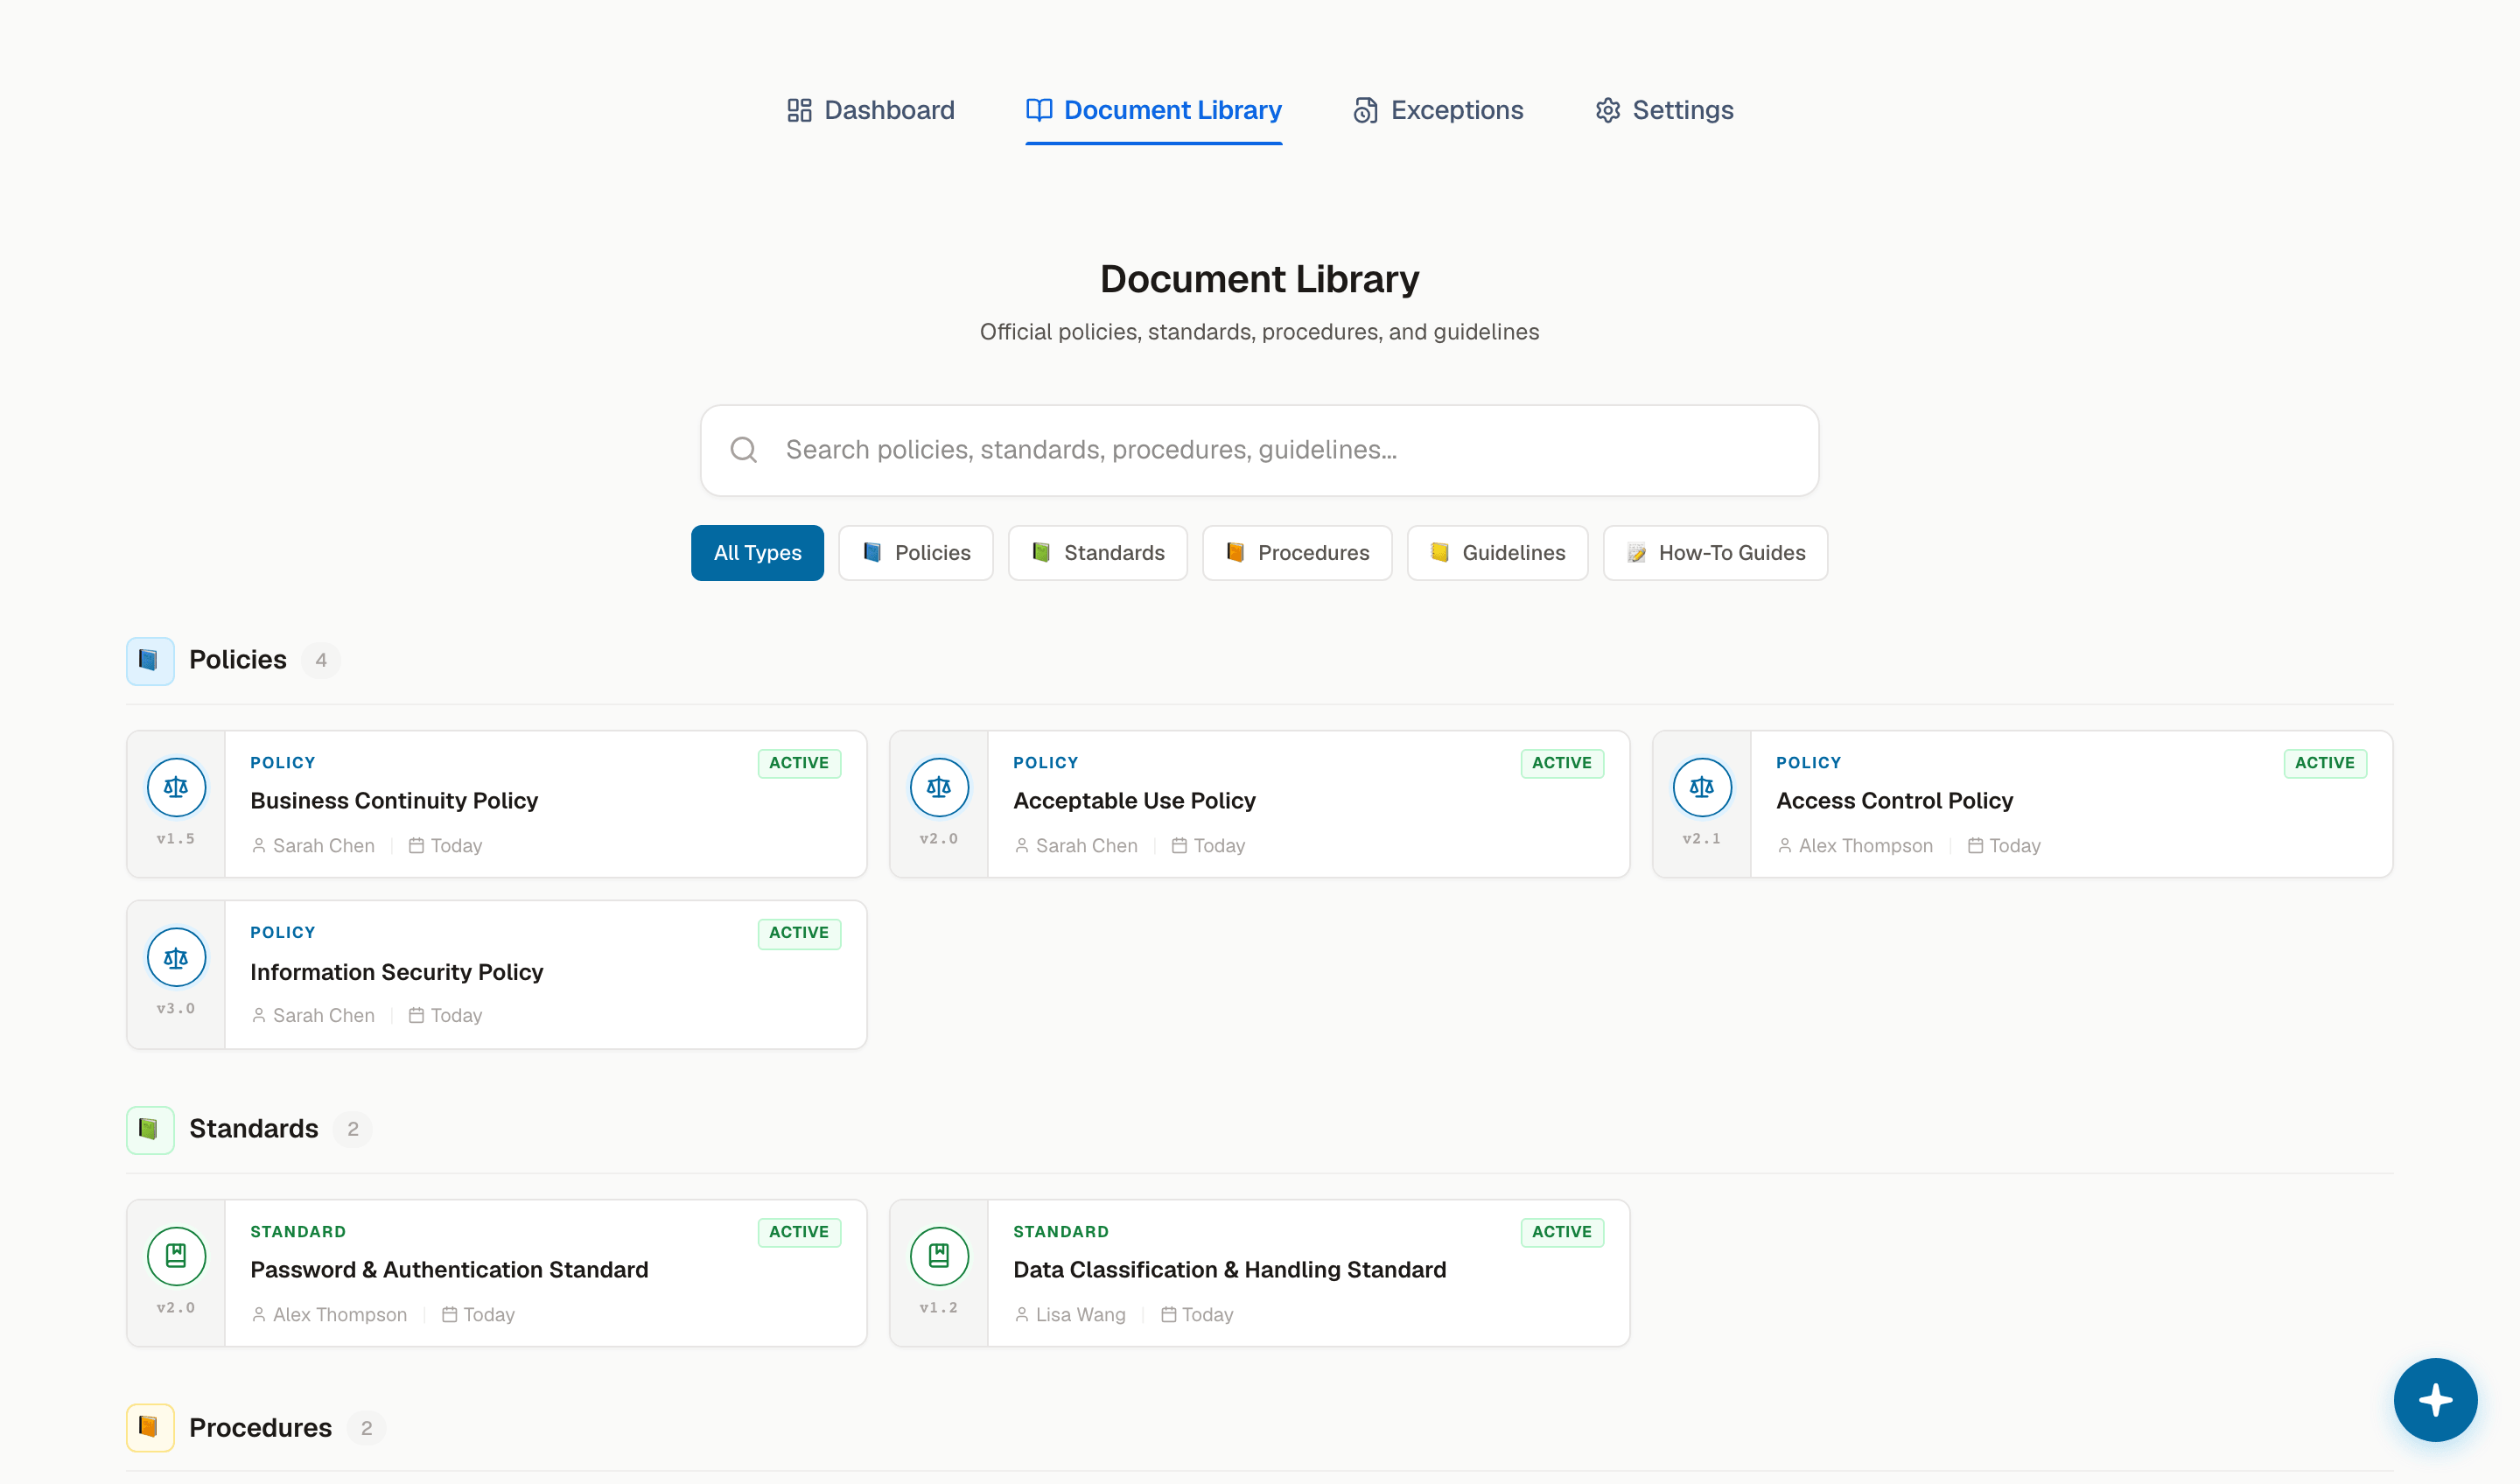
Author, approve, and attest in one place. Policies carry version history and link to the controls they govern, with exceptions tracked instead of forgotten.

Author, approve & attestVersion historyExceptions tracked
Explore Policy
app.alvor.io/policies
The policy document library with policies, standards, and procedures

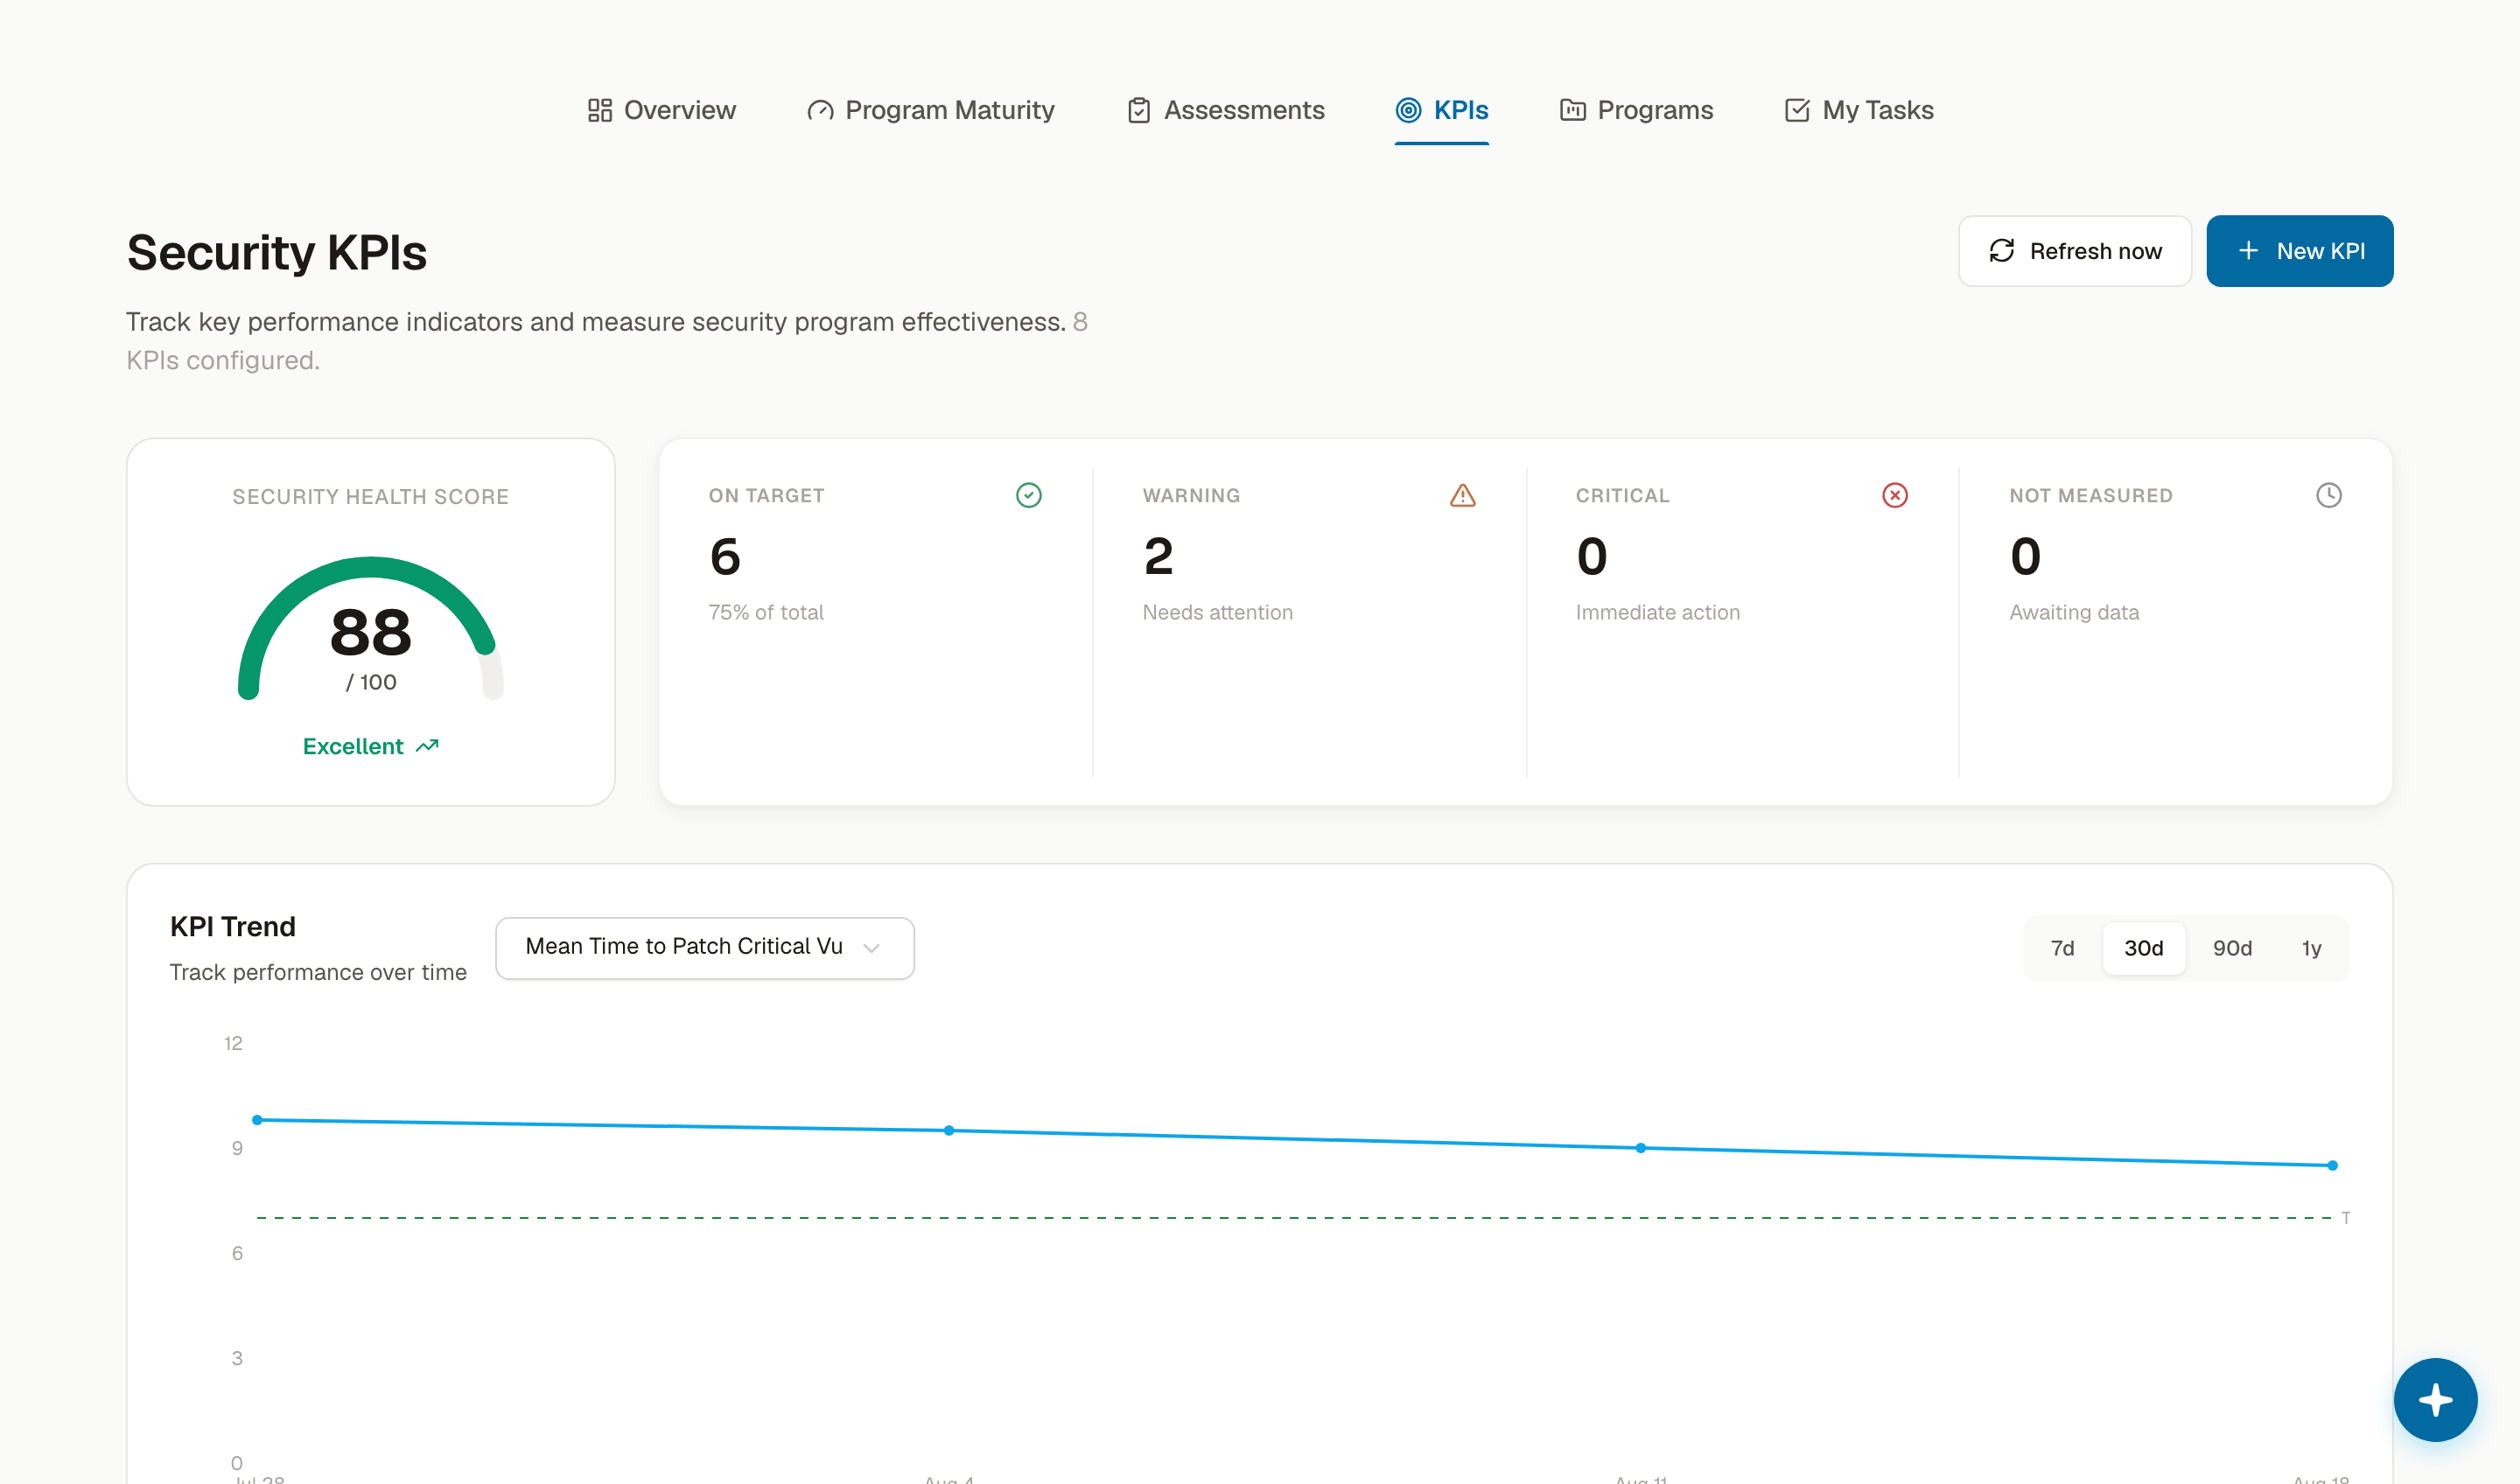
The program layer: plan the work, track KPIs, and run maturity assessments against the frameworks you care about. What the board asks, this module answers.

Program planningKPIsMaturity assessments
Explore Security Management
app.alvor.io/security-management
Security program KPIs tracked against targets

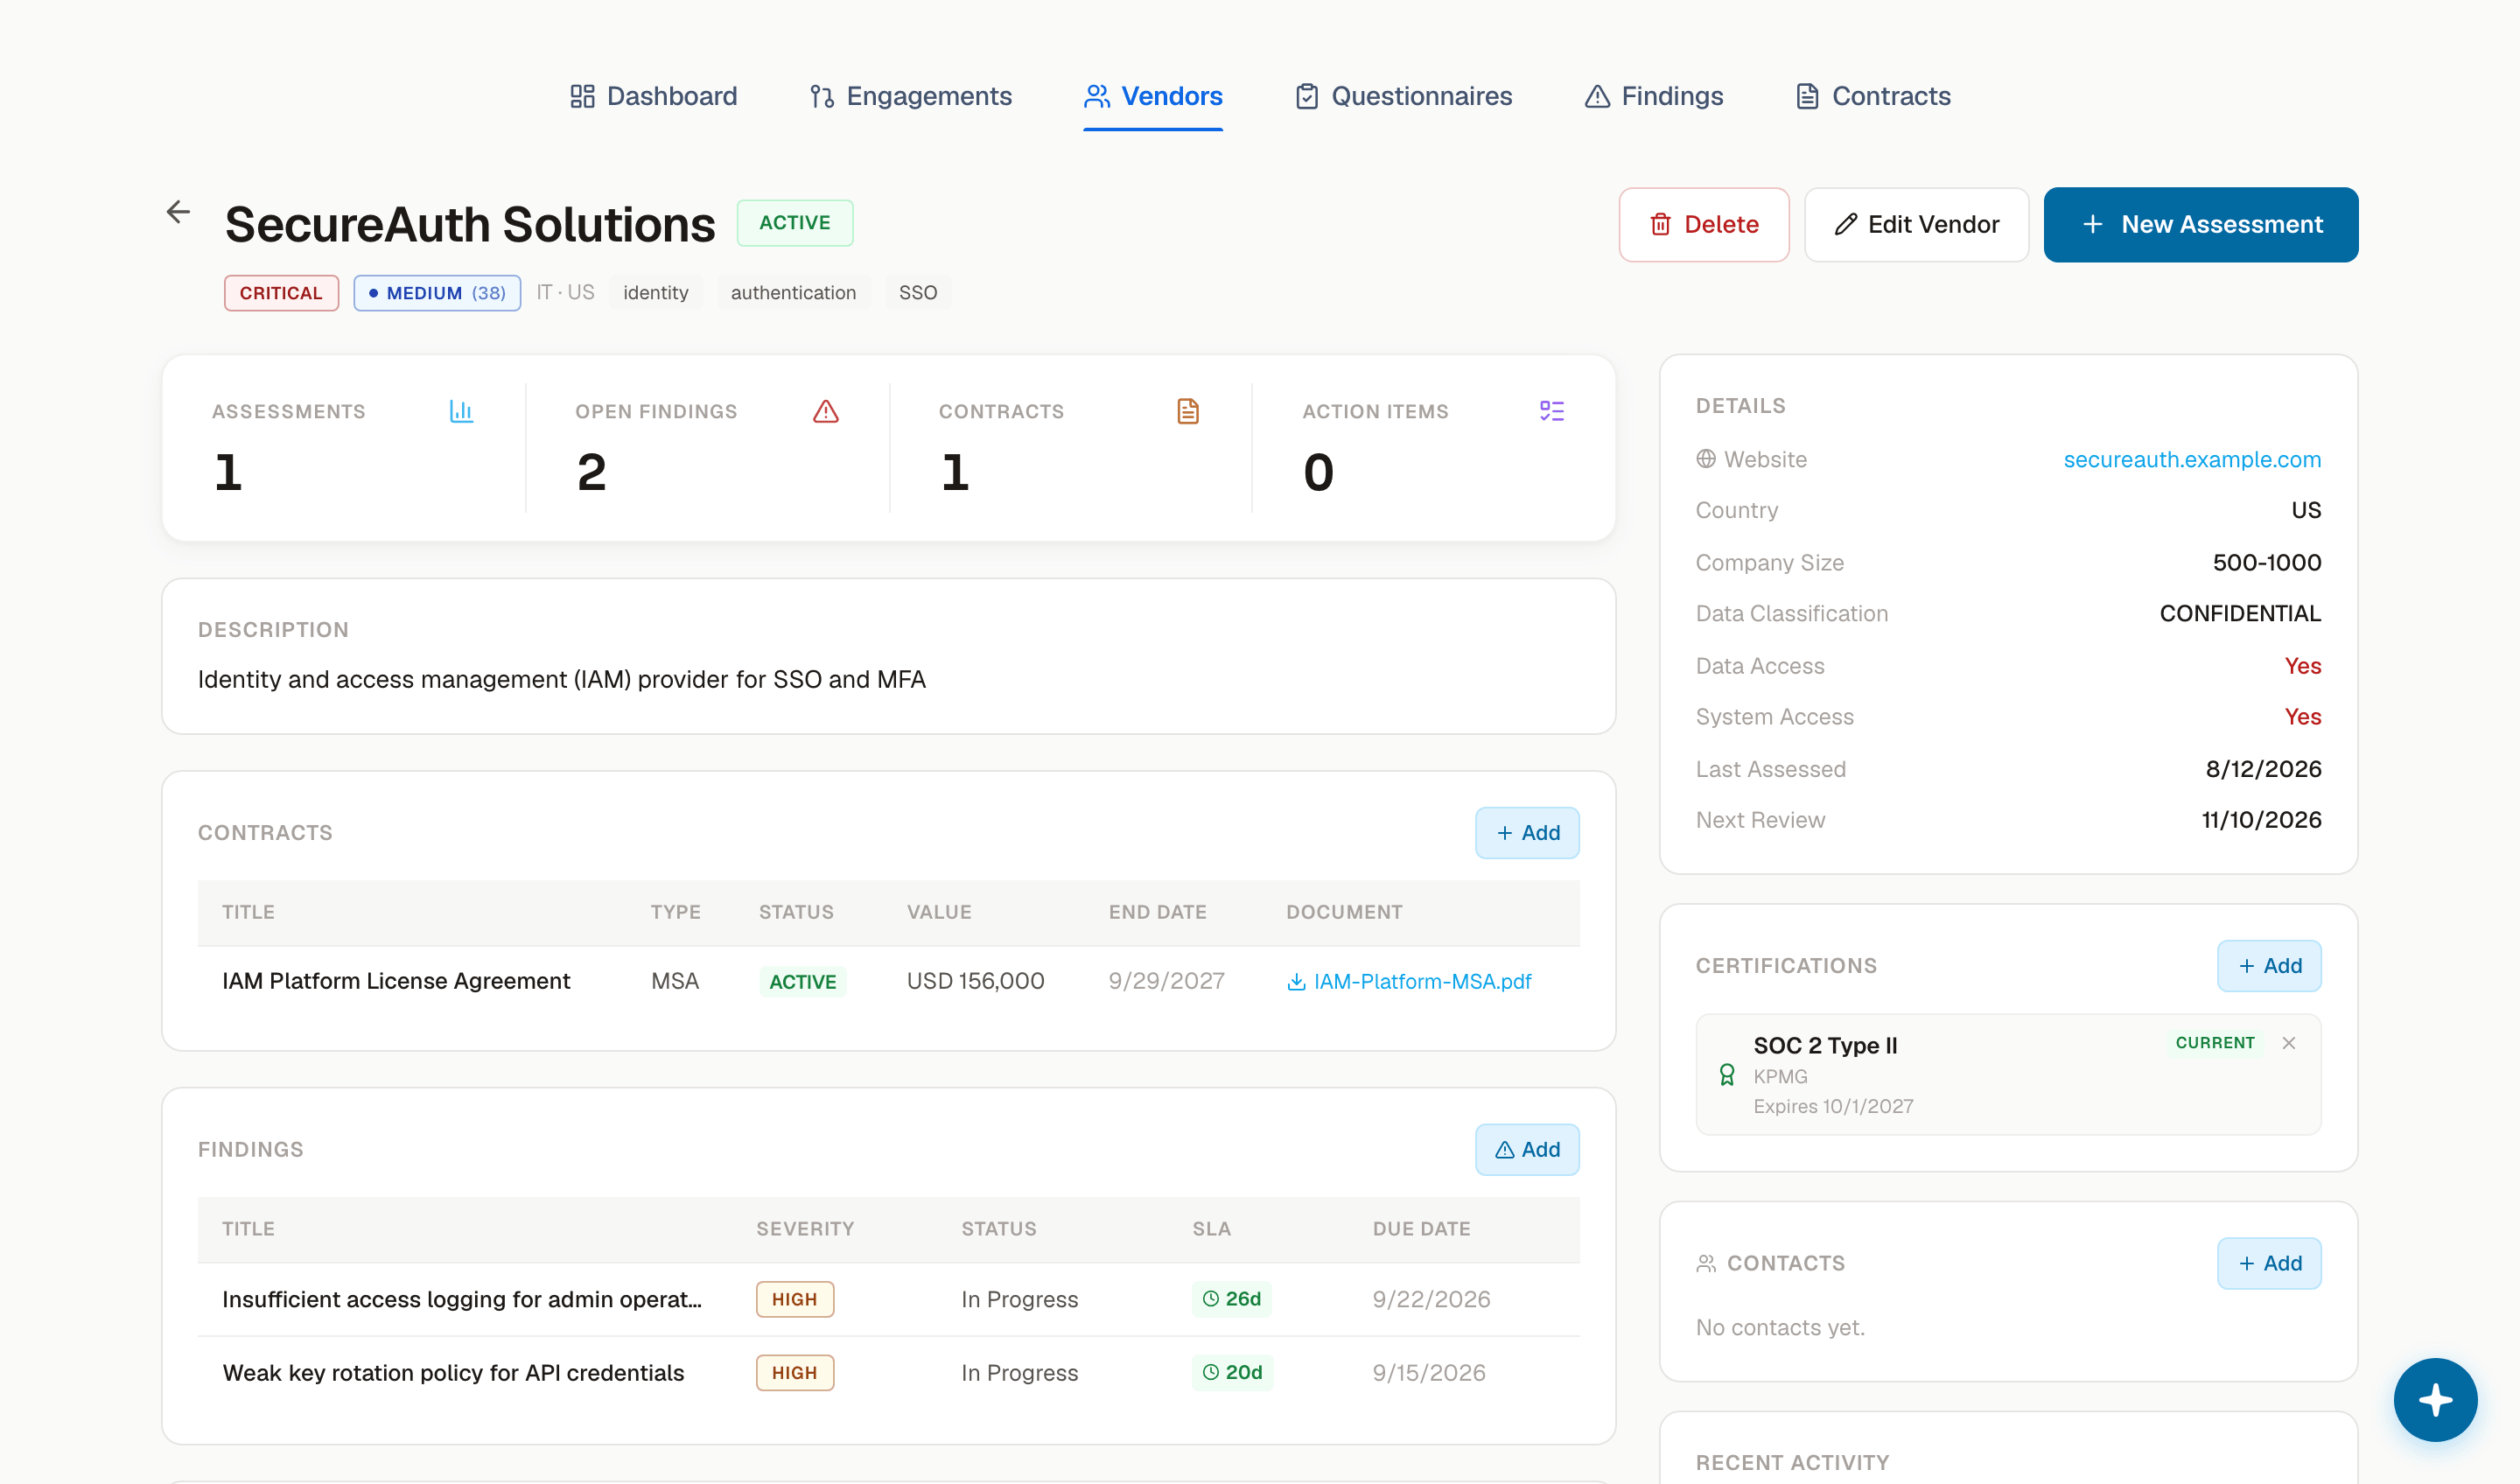
One structured assessment, findings with SLAs, contracts and certifications in a single vendor record. Third-party risk handled like your own.

One structured assessmentFindings with SLAsAnswered in a portal
Explore Third-Party Risk Management
app.alvor.io/vendors
A vendor record with assessments, findings, contracts, and certifications

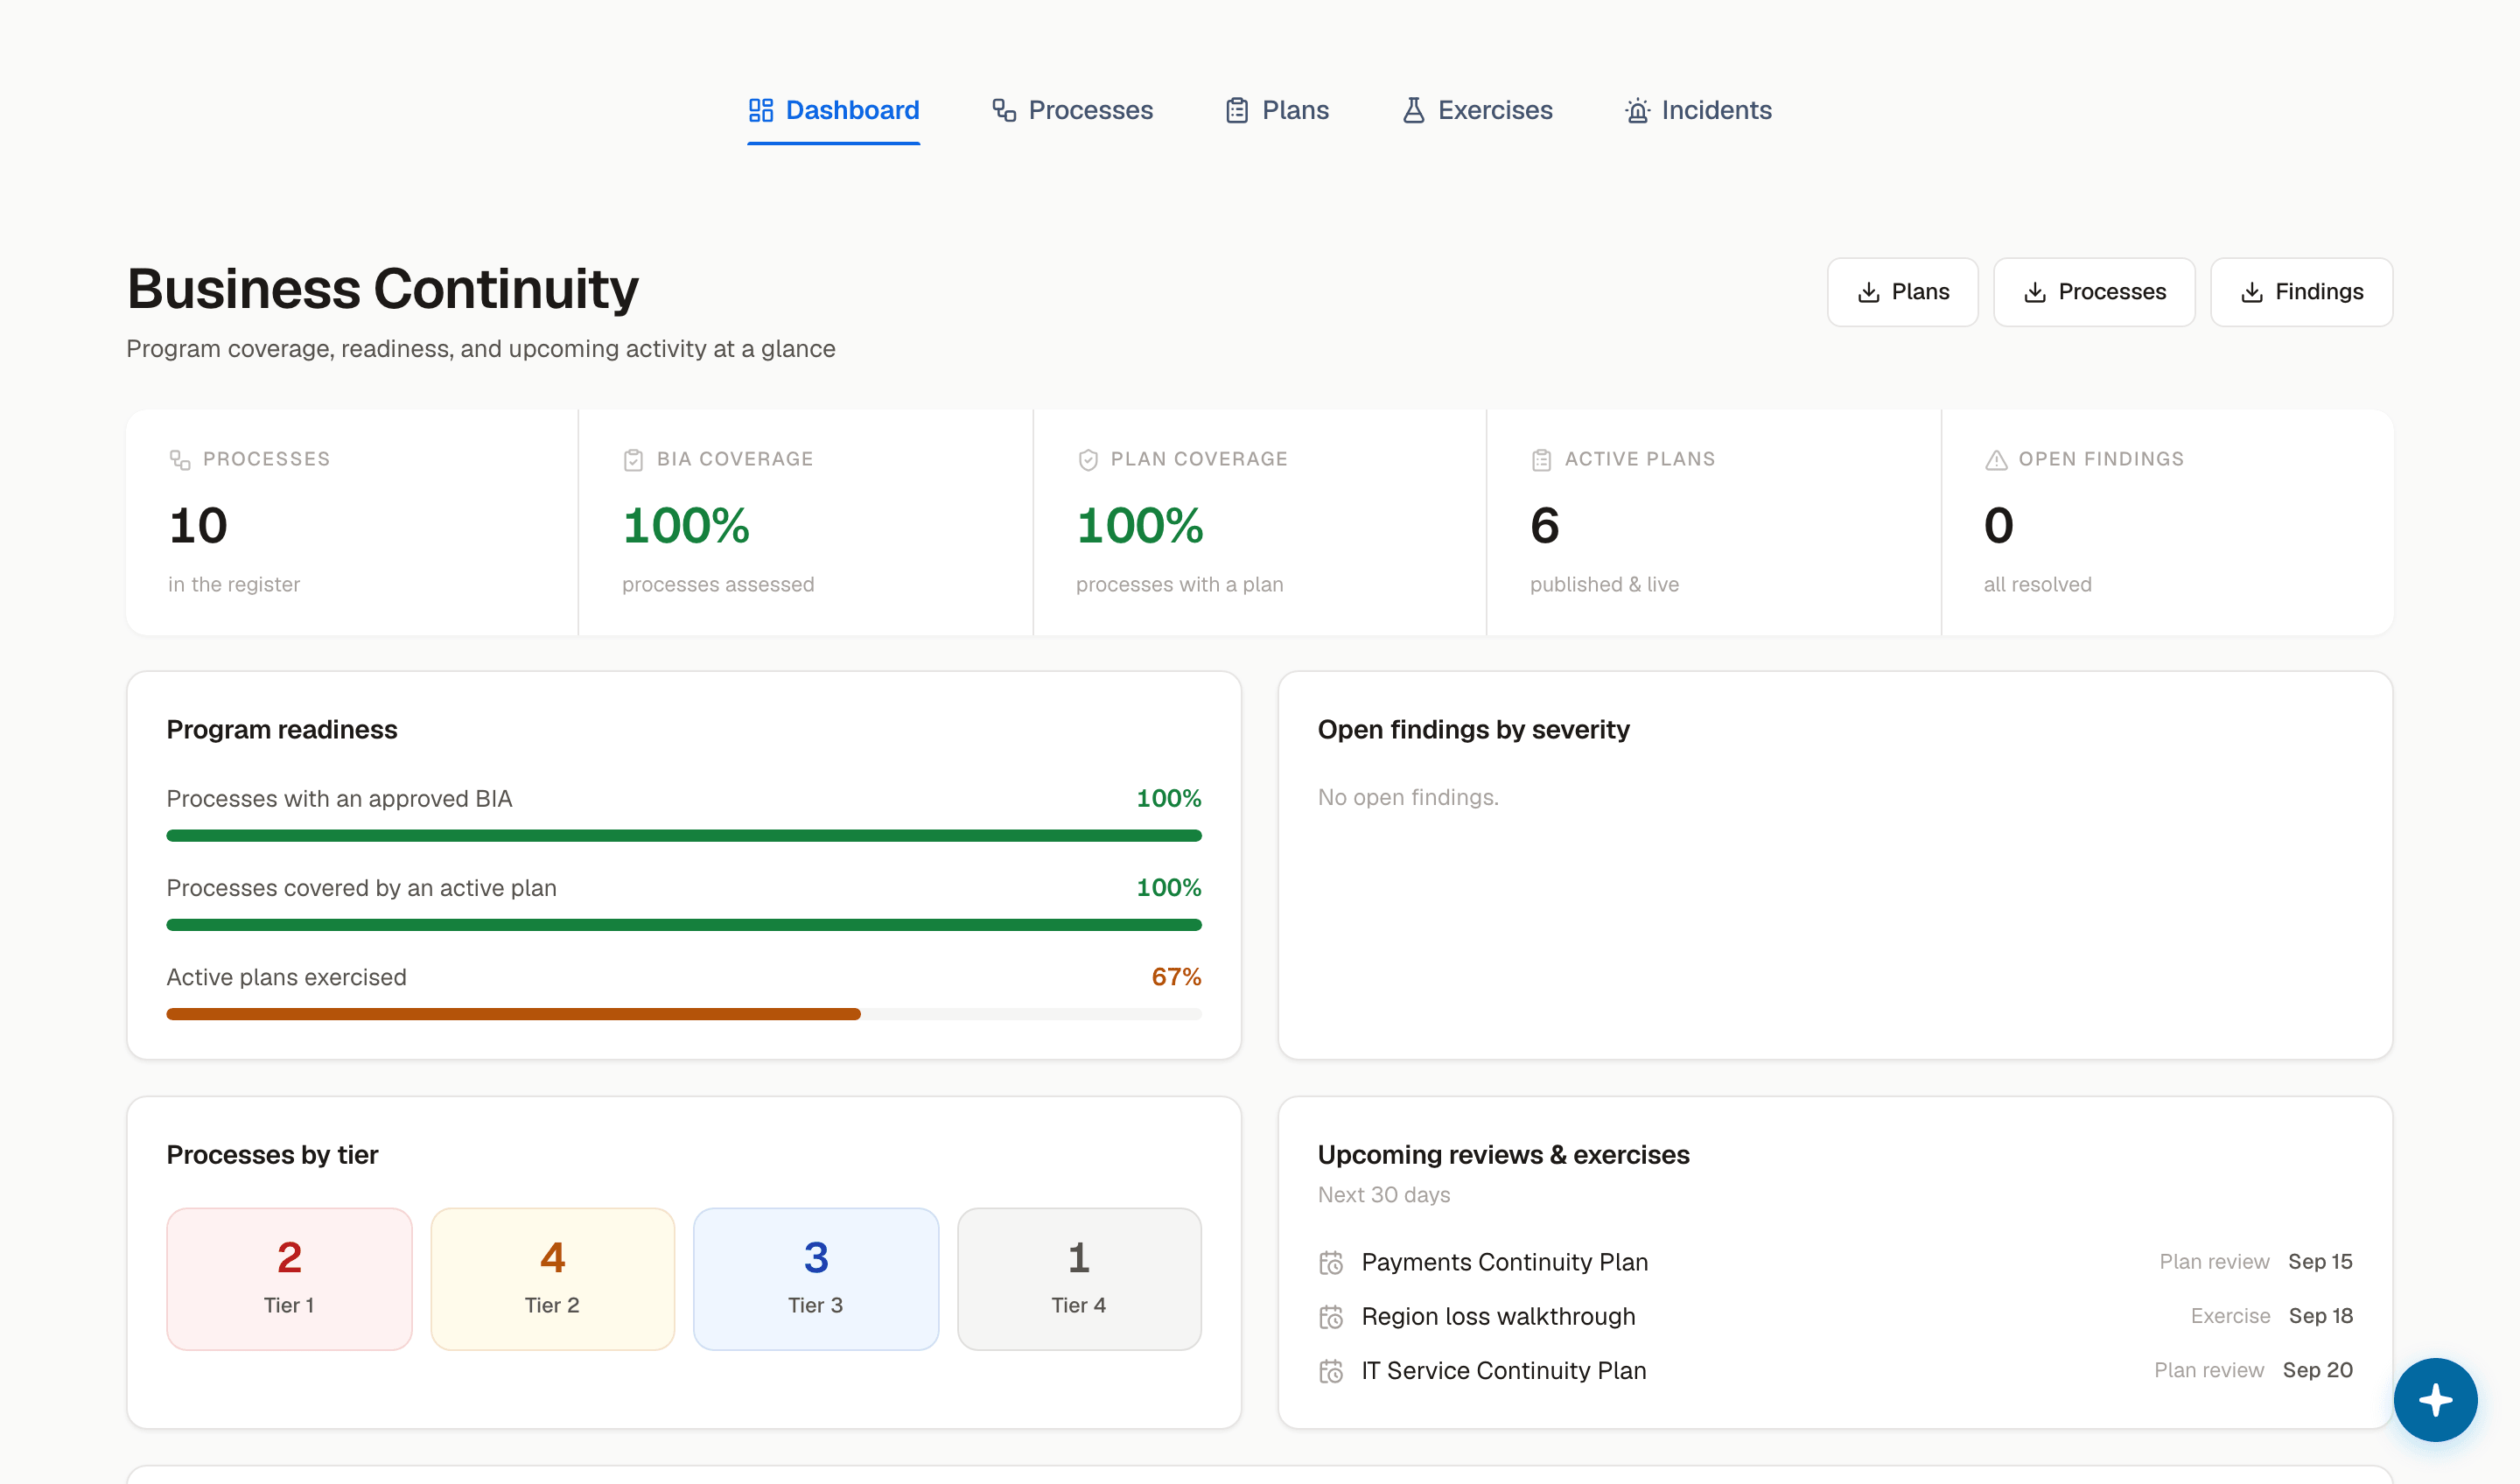
Business impact analysis, continuity plans, and exercises, tied to the same asset register as everything else. When something breaks, the plan knows what it protects.

Business impact analysisPlans & exercisesReadiness tracking
Explore Business Continuity
app.alvor.io/business-continuity
The business continuity dashboard: BIA and plan coverage, readiness, and upcoming exercises

What the record looks like on screen

Sample data throughout. Every label and state is the product's own, and each card opens a real screen from the same module.

Example: a risk acceptance approved by its named Business Owner, with conditions, a scope, an expiry date and the residual score saved at the decision.

Only the named person can accept a risk

The requester nominates a Business Owner, System Owner or CISO. Only that person can approve, with conditions, a scope and an expiry date, and the residual score is saved at the moment of the decision.

Explore Risk Management

Example: a risk drafted by the AI Assistant and approved by a person, with the approval written to the audit log.

The assistant drafts the change, and a person approves it

Every write the assistant proposes waits for a person to approve it. The approval is written to the audit log, and the assistant runs on your own model.

Example: an acknowledgement campaign for version 4 of a policy, showing who has acknowledged it and when.

Prove who acknowledged each version, and when

Run an acknowledgement campaign for each published version, with a due date and reminders. Each acknowledgement records the person, the time, the IP address and the session.

Explore Policy

Example: one control mapped to ISO 27001 and NIST CSF 2.0, each with its own status, sharing one piece of evidence.

Map one control to every framework it satisfies

Attach evidence to the control once and reuse it across ISO 27001, NIST CSF 2.0 and any framework you map it to. Each framework keeps its own status, assessed against its own wording.

Explore Compliance

What you can hand an auditor, and the standards behind it

The method and the output, both from the product.

  • ISO/IEC 27001:2022Installed with its control text
  • NIST CSF 2.0Crosswalks from NIST's informative references
  • MITRE ATT&CKThe threat library behind risk
  • STRIDEThreat modelling in Secure by Design
  • Your own frameworkAdded in its publisher's structure

Statement of Applicability

Which controls apply and why, on screen and as a CSV for the auditor.

Compliance

Risk register export, with its Criteria sheet

Your likelihood labels, impact dimensions and matrix travel with the register.

Risk Management

The design project PDF

The business impact analysis, diagrams, threat tables and sign-off matrix in one branded document.

Secure by Design

Get started

See how Alvor works for your role

Whether you lead security, run IT, manage compliance, or sit in the C-suite - we'll show you your view.