Policy
Your governance
documents live in
shared drives. Nobody
reads them.
Alvor centralises every policy, procedure, standard, and desk guide in a single governed library - with version control, structured approval chains, signature tracking, and automatic renewal alerts. Every document has a complete audit trail.
Who it is for
A policy nobody read is a policy you do not have.
The security lead
Policy that maps to the controls you are actually assessed on.
- A policy maps to one or more compliance controls with notes
- Immutable published versions, with a trail when one is retired
- Structured approval chains with a recorded sign-off
Everyone else
Attestation that works like any other task.
- A campaign with a due date and reminders
- A document to read and one acknowledgement to record
- Time, IP and session captured on the acknowledgement
The compliance lead
Exceptions that expire instead of quietly becoming permanent.
- An exception attaches to one or many policy documents
- Exceptions run to expiry and renewal, not to forgetting
- The Draft Studio hands outline and content to the editor for review
The lifecycle
Every policy moves through seven stages.
Every policy follows the same structured path from authoring through retirement. No silent approvals, no version confusion, no gaps in the audit record.
04
Version bump, go live
Approved policies go live with a version bump. Previous versions are archived with full diff. Stakeholders are notified. Acknowledgment campaigns auto-trigger.
The product
What that looks like on screen.
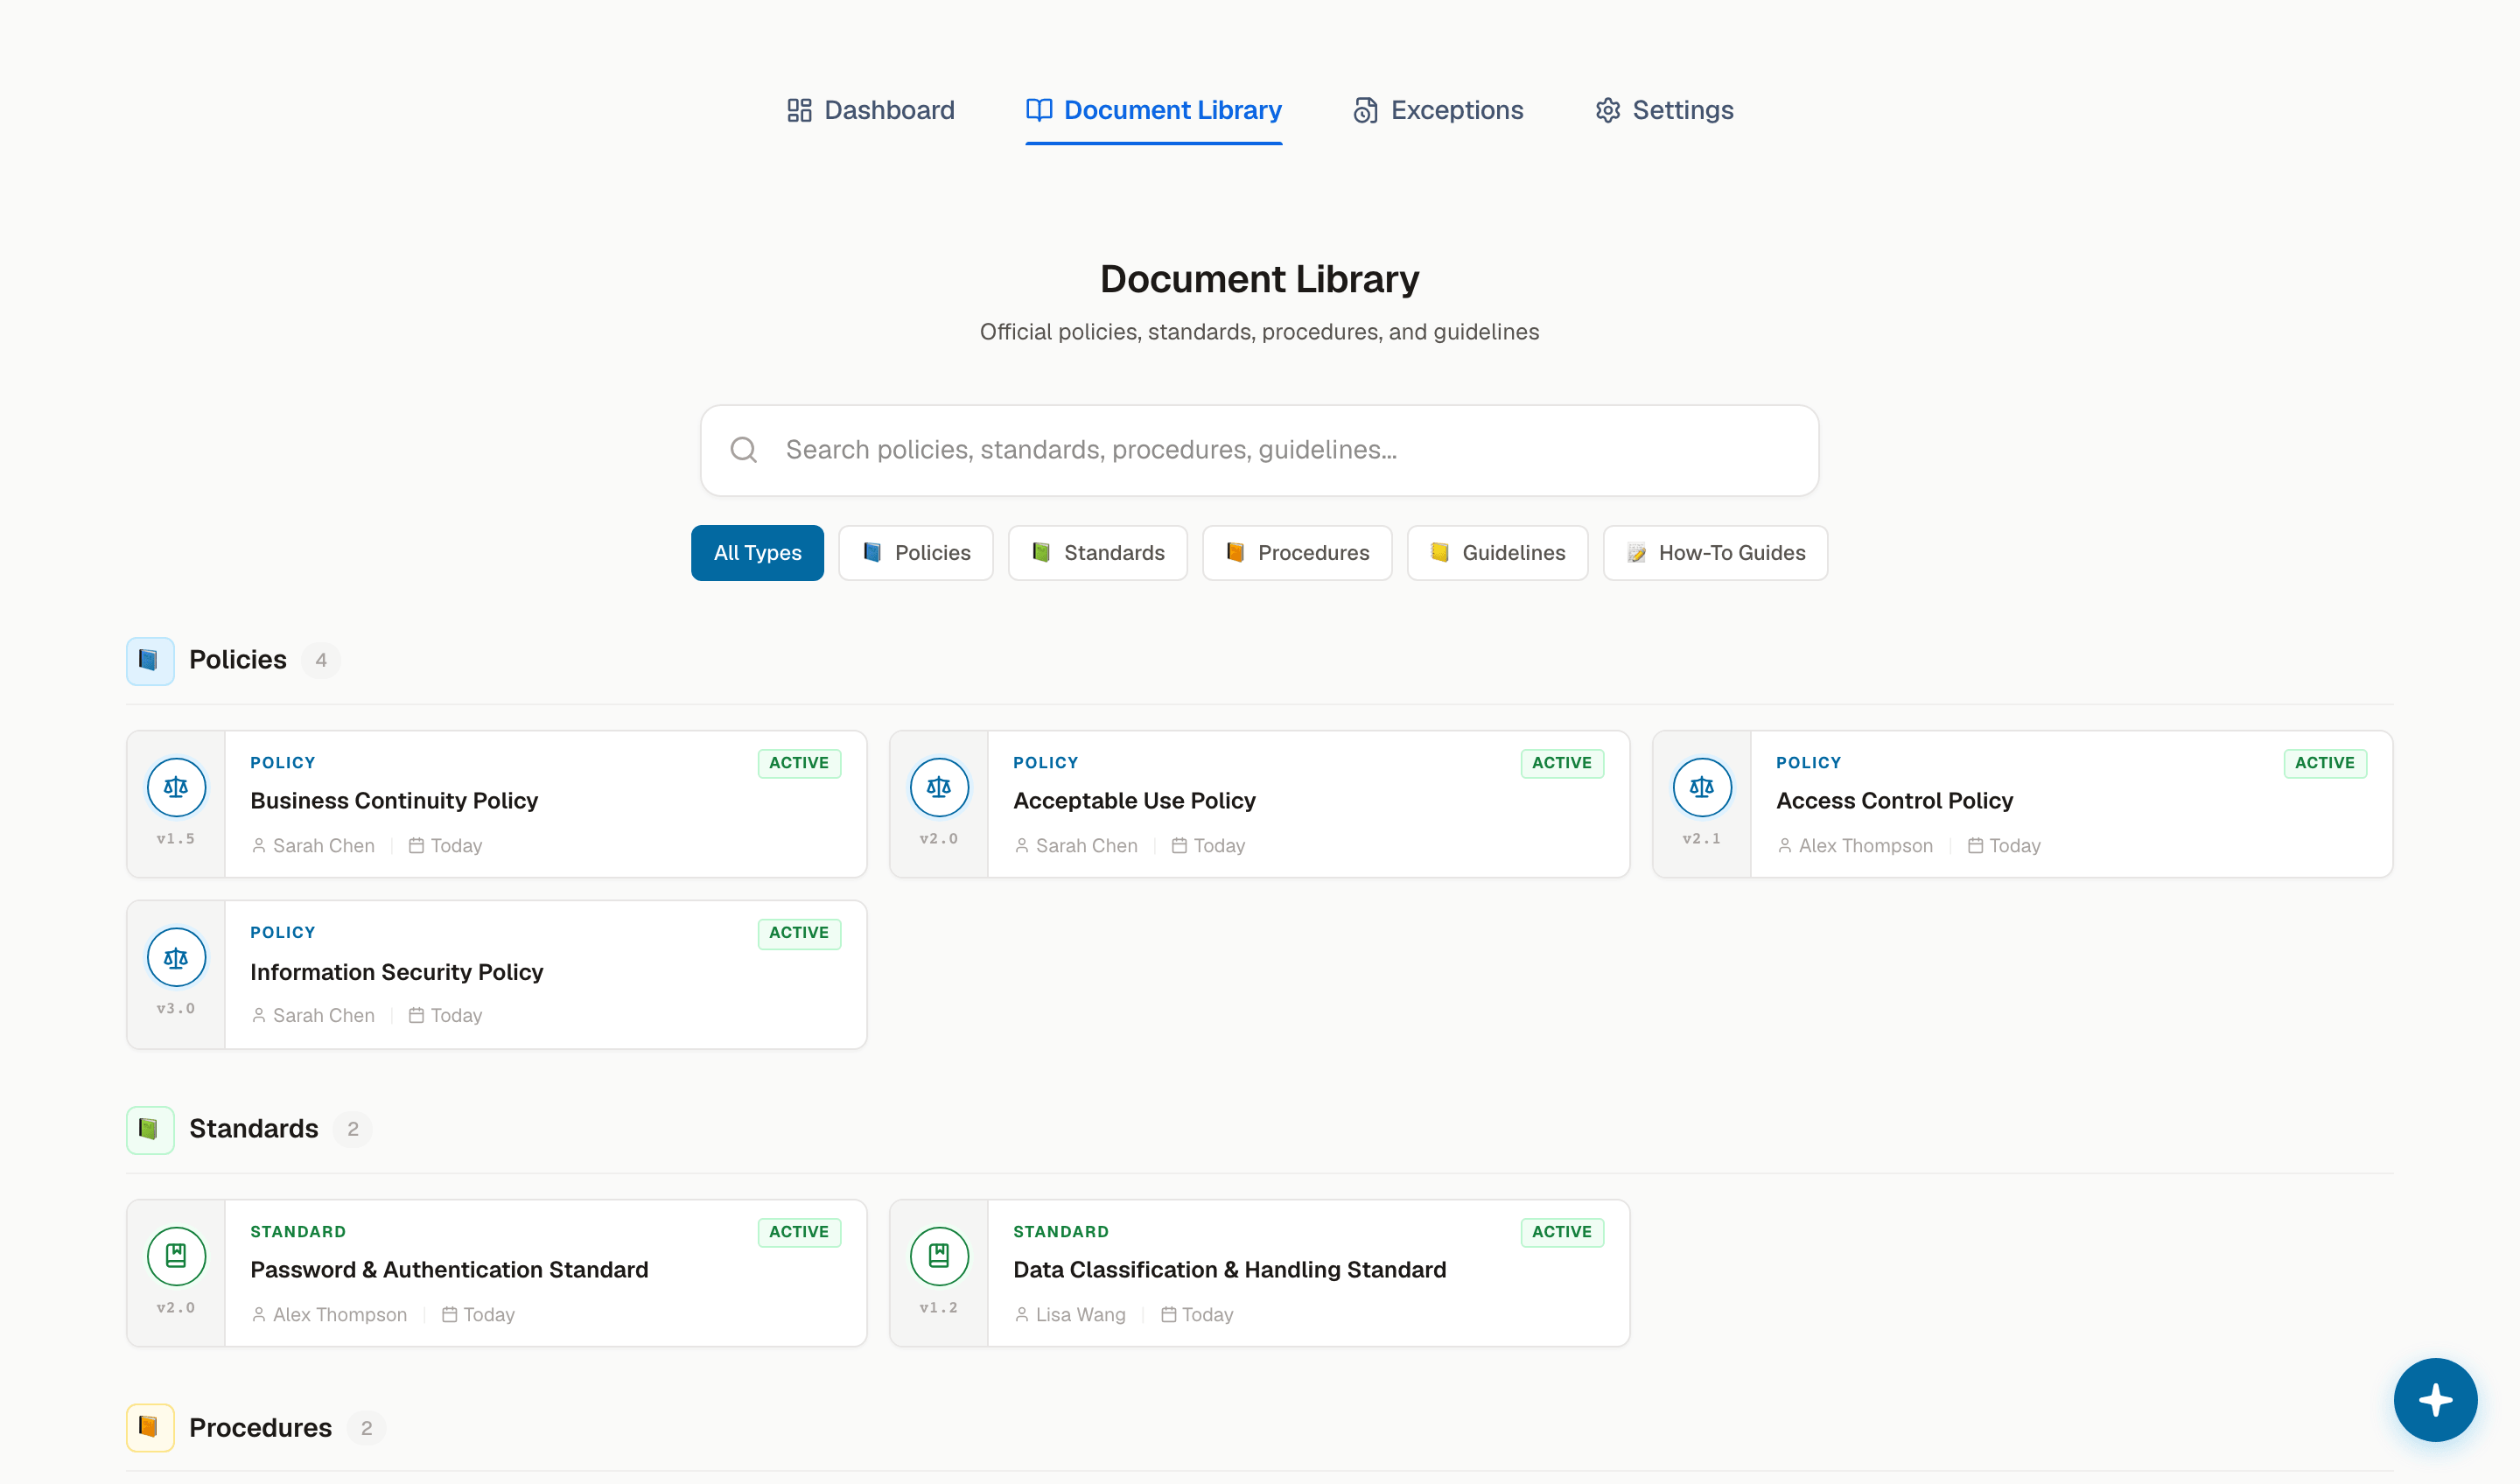
01 · The library
Every policy, its version, and who has acknowledged it
The current published version of each document, the campaign attached to it and how far through the organisation that campaign has got. Acknowledgement is recorded per person with time, IP and session, so proving engagement is a query rather than an exercise.
app.alvor.io/policies
Draft with AI
The draft is no longer the slow part.
The Policy Draft Studio interviews you first: organization, industry, audience, target frameworks, risk posture, review cadence. Then it proposes the document properties, an outline, and the full content, grounded in the compliance controls you have loaded rather than in generic boilerplate.
Nothing saves itself. Each step lands in the editor when you click Apply, and the finished document goes through the same review, approval, and acknowledgement flow as any other policy.
Access Control Policy
DraftDraft with AIProposed outline
1Purpose and scope
2Roles and responsibilities
3Access provisioning and deprovisioning
4Privileged access
5Review cadence and exceptions
Grounded in · ISO 27001 A.5.15, A.5.18 · SOC 2 CC6.1
Apply outlineRevise
Policy Registry
All your policies in one registry
See your entire policy landscape at a glance. Filter by type, status, owner, or compliance framework. Know instantly what's published, what's in review, and what's overdue.
- 8 policy categories with configurable taxonomy
- Real-time status tracking across all documents
- Linked compliance frameworks per policy
- Review schedule tracking with overdue alerts
Information Security
Published4documents
Acceptable Use
Published2documents
Data Classification
In Review3documents
Incident Response
Published2documents
Access Control
Published3documents
Vendor Management
Draft2documents
Remote Work
Published1document
BYOD
Under Exception1document
Acknowledgments
You distributed
the policy. But did
anyone read it?
Acknowledgment campaigns target the right people and prove they engaged. Department-level dashboards show completion rates, and automated reminders chase down stragglers before auditors do.
- Target by department, role, location, or individual
- Read receipt with timestamp and IP for audit
- Automated 3-stage reminders before deadline
- Manager escalation for overdue acknowledgments
Acknowledgment Campaign
Q1 2026 - All Hands
92%
overall
Engineering94/102
Product38/41
Operations27/28
Sales52/67
Legal12/12
Auto-reminders: 7d, 3d, 1d before deadline · Escalation after 48h overdue
Governance Library
Every governance document: shared, signed, and tracked.
Policies, procedures, standards, and desk guides - maintained in a single library and distributed to the right people. Staff always see the current version. Alvor records every signature with a timestamp and notifies owners before review and renewal dates arrive.
Policies
18
Statements of intent and direction
Procedures
34
Step-by-step operational instructions
Standards
12
Technical and process specifications
Desk Guides
27
Role-specific quick reference cards
Signature log
MR
Maya R.
Mar 28 · 10:14 AMCISO
Signed: InfoSec Policy v4.1
TK
Tom K.
Mar 27 · 3:42 PMEngineering Lead
Signed: Access Control Procedure v2.0
PS
Priya S.
Mar 26 · 9:01 AMHead of Compliance
Signed: Data Classification Standard v1.3
Every signature is captured with a timestamp, device, and document version - ready for any audit.
Upcoming reviews & renewals
Remote Work Policy v2.1
Review due
BYOD Standard v1.0
Renewal due
Acceptable Use Policy v3.0
Review due
Alvor sends automatic notifications at 60, 30, and 7 days before each document's review or renewal date - so nothing lapses.
Exception Management
Not every team
can comply right
away. Exceptions
are tracked, not
ignored.
Every exception is formally requested, risk-assessed, approved with compensating controls, and given a hard expiration date. Nothing is ad-hoc. Nothing lives forever.
- Formal request with business justification
- Compensating controls documented per exception
- Time-bound expiry with automated reminders
- Risk acceptance linked to the parent policy
Exception Register
Active exceptions
3 active1 expiring
Temporary admin access for migration
Information Security Policy v4.0
OwnerR. Lee
Controls3
RiskHigh
93% of exception period elapsed
1 day left· expires Apr 1, 2026
Legacy SSO bypass for SAP integration
Access Control Policy v3.2
OwnerM. Chen
Controls2
RiskMedium
49% of exception period elapsed
91d left· expires Jun 30, 2026
Extended data retention for regulatory hold
Data Classification Policy v2.1
OwnerJ. Park
Controls1
RiskLow
11% of exception period elapsed
168d left· expires Sep 15, 2026
Risk distribution
High
1
Medium
1
Low
1
All exceptions carry documented compensating controls and a hard expiry date. No exception is open-ended.
What it replaces
Policies that can prove they were read.
Most policy programs can produce the document. Far fewer can produce evidence that the organisation saw it.
Instead of
Policies in a shared drive
No version anyone trusts, and no record of who opened which one.
In Alvor
Immutable published versions with a structured approval chain behind each one.
Instead of
Attestation in a survey tool
A second system, a second export, and a join nobody wants to do at audit.
In Alvor
A campaign with reminders, one acknowledgement per person recorded with time, IP and session.
Instead of
Exceptions in an email thread
A temporary carve-out that becomes permanent because nothing expires it.
In Alvor
Exceptions attached to the policies they touch, running to expiry and renewal.
How it connects
These are the exact links in the data model.
Named precisely, because “everything connects to everything” is not a claim anyone can check.
Policy
Policies people actually acknowledge - and auditors actually trust
Alvor turns static documents into living policies with structured approval chains, targeted acknowledgment campaigns, version history, and formal exception tracking. Every policy is governed end to end.